Cyber researchers broke into OpenAI using its key rival Anthropic’s software, highlighting vulnerabilities in the ChatGPT maker’s security as leading AI companies face mounting scrutiny over safety.
A small cyber security group gained access to an OpenAI employee’s ChatGPT account, which permitted them to read private software information and suggest changes.
The researchers had been given access to an Anthropic tool specifically designed for security professionals, and were paid for the work as part of a program to find vulnerabilities before they could be exploited by bad actors.
Hegseth’s Theology and the Question: What Would Jesus Do?
There is a question Christians have been asking for generations: What would Jesus do?
It is a deceptively simple question that is printed on bracelets and bumper stickers, taught to children in Sunday schools, and invoked when Christians are discerning how faith should shape public life. The question becomes considerably more demanding when the decisions at stake concern war, immigration, poverty, political power, and the use of military force.
In addition to the recent attention about his military strategy, social and political beliefs, and leadership style, Pete Hegseth’s public theology deserves serious attention from those unfamiliar and disinterested in religion as well as adherents of Christianity.
As secretary of defense, Hegseth has increasingly spoken about American power in explicitly Christian language. He has hosted Christian worship at the Pentagon, invoked Scripture in connection with military service, emphasized the Christian foundations of the United States, and described some Trump administration policies — including border enforcement — as “biblical.” Indeed, speaking at a Christian media convention last February, Hegseth connected the health and founding of the United States with Christianity and characterized border and immigration policies as mandated in the Bible.
The question about Hegseth’s faith and religious practice, however, cannot simply be whether he is sincere. The question is more fundamental: What kind of Christianity is being proclaimed when the language of Jesus is attached to military power? Or perhaps a simpler but harder question: In the face of war, authoritarianism, economic, environmental, and political crises: What would Jesus do?
A Christianity of Power
The Christian faith has always contained competing visions of what it means to follow Jesus. There is a Christianity that blesses kings, armies, empires, and national ambitions. There is another Christianity that remembers a Palestinian Jewish leader who was unhoused and a migrant and was executed by an imperial power after heralding the arrival of a radically different kingdom. This distinction matters a great deal.
Hegseth routinely emphasizes strength, warriors, national identity, borders, enemies, and divine blessing. And joining forces with Israel to prosecute the war with Iran has only heightened the stakes of his rhetoric. Early in the conflict, Hegseth cited Psalm 144, including its language about God training hands for war and fingers for battle.
There is nothing inherently un-Christian about a person in the military having a sincere religious faith. People of faith serve in the armed forces for many reasons. Generations of religious scholars and adherents have considered war and conflict as it relates to the faith through theories and practices of religious pacifism, “just war,” defensive war, theologies of self-defense, conceptions of the last days, and the ethical limits of violence in humanitarian conflicts, among others. The theological problem arises, however, when the power of the state begins to present itself as an instrument of God’s purposes.
That is a very old temptation.
Empires have long claimed divine sanction. Kings have declared their wars holy. Nations have wrapped their ambitions in sacred language. And Christians have at times sought to confuse the interests of the nation with the kingdom of God. But Jesus does something profoundly disruptive to this arrangement: He refuses to identify God with Caesar.
The People at the Margins
Consider where Jesus directs our attention. Throughout the Bible, Jesus embraces people whom those with power, military might, and wealth have pushed aside: the poor, the sick, the imprisoned, immigrants, women, children, tax collectors, and those treated as religious outsiders.
In Matthew 25, one of the most famous Bible passages — sometimes called the “Last Judgment” — Jesus identifies with the hungry, the stranger, the naked, the sick, and the imprisoned. “Whatever you did for one of the least of these,” he teaches, “you did for me.”
That is not an incidental teaching. It is a political and theological reorientation. And it is directed at nations, not simply individuals or religious congregations.
Jesus asks: How has your nation treated the most vulnerable among you?
The question Jesus asks his followers is not first, “How strong is your nation?” It is not, “How effectively have you defeated your enemies?” It is not even, “How faithfully have you defended your borders?” Instead, he asks: How has your nation treated the most vulnerable among you? This matters enormously when Christian language is used to justify violent and exclusionary immigration policy or when it is used to promote cutting off families from food or lifesaving healthcare.
If we claim that border enforcement is “biblical,” then Christians must practice the Bible’s extraordinary insistence on welcoming the other. After all, Scripture commands God’s people to remember that they, too, were once strangers in a foreign land, and the way to honor and worship God is by welcoming the immigrant neighbor. If Matthew 25 means what Christians have traditionally claimed, Christ is encountered precisely among the hungry, the unhoused, the incarcerated — and that as long as anyone is unfree and impoverished, it is the responsibility of the nation to do something about it.
Theology of the Enemy
There is another problem with a Christianity centered on military strength: its understanding of the enemy. Christianity does not teach that some people become less human because they are someone’s adversaries. It does not profess that God blesses battleships nor justifies genocide (even if Hegseth’s spiritual adviser claims it does).
Jesus does not say, “Love your friends and destroy your enemies.”
Jesus’s command to love one’s enemies may be among the most difficult teachings in the entire New Testament. It is also one of the clearest.
Jesus does not say, “Love your friends and destroy your enemies.” He says, “Love your enemies and pray for those who persecute you.”
Jesus does not say, “Blessed are the powerful because they shall dominate.” He says, “Blessed are the peacemakers for they shall be called the descendants of God,” and “Blessed are the poor for they shall be first under God’s reign.”
That does not mean that people of faith must be naïve about violence. It does not mean governments face no genuine security threats. It does not erase the moral complexity of protecting human beings from violence. But it does mean that people who call themselves Christians should be extraordinarily cautious whenever military violence is described as holy, righteous, inevitable, or divinely ordained.
Christian tradition contains a long history of wrestling with war. It also contains an even deeper tradition of martyrs, peacemakers, conscientious objectors, abolitionists, human rights activists, and nonviolent movements that have insisted that human beings cannot be reduced to enemies.
On “Christ Is King”
One phrase that increasingly appears in Hegseth’s public religious rhetoric is “Christ is King.” On the surface, this is an ancient Christian confession. But Christians should be careful about what happens when it is fused with nationalism. If Christ is King, then Caesar is not. If Christ is King, then the nation cannot be God. If Christ is King, then military might cannot be the ultimate measure of righteousness. And if Christ is King, then Christians must remember what kind of king Jesus was.
“You Only Get What You’re Organized to Take,” by Liz Theoharis and Noam Sandweiss-BackAvailable on Bookshop.org.
Jesus did not arrive in Jerusalem on a tank. He did not establish his kingdom through an air campaign. He did not recruit an army to seize the Roman state. Jesus entered the city on a donkey. He washed his disciples’ feet. He touched people considered untouchable. He fed hungry crowds. He stood with the condemned. And when his disciples reached for weapons, Jesus told them to put them away. This is not weakness; it is a different conception of power and a different idea of violence, military and force. And it stands worlds away from the Hegseth’s professed belief in a conquering Christ.
Christian nationalism raises the question of who counts as part of the nation — and, implicitly, who counts as part of the Christian community. Hegseth’s religious politics have attracted scrutiny because of his association with a conservative Reformed Christian milieu and his willingness to amplify figures and institutions associated with Christian nationalist ideas. That should concern Christians not because Christianity should be banished from public life, but because Christianity is too important to be reduced to a tribal identity. There is no nationalism in the Sermon on the Mount; there is no exceptionalism in the Last Judgment.
Christianity offers an alternative to nationalism that does not require Christians to abandon love of country, but it begins by refusing to worship their nation.
Jesus did not teach his followers to build communities divided by race, citizenship status, wealth, or political loyalty. The early Christian proclamation was astonishing precisely because it created a community in which Jew and Greek, slave and free, male and female could belong together.
Christianity becomes spiritually dangerous when it is transformed from a call to discipleship into a badge of national membership, and a cross becomes something very different when it is used to sanctify exclusion, violence, and war, especially against the poor and marginalized.
So, What Would Jesus Do?
Let’s stop treating “What would Jesus do?” as a sentimental slogan. Instead, ask the question concretely.
What would Jesus do when a family fleeing poverty and violence arrives at the border?
What would Jesus do when a child is separated from a parent?
What would Jesus do when a nation considers going to war?
What would Jesus do when military personnel are asked to kill (and the nation suggests canceling student debt to those who sign up to do that killing)?
What would Jesus do when poor communities are abandoned while enormous resources flow into weapons?
What would Jesus do when a government claims God has blessed its political program?
And what would Jesus do when Christians begin to believe that their nation has a special claim on God?
The Gospels give us clues. Jesus runs toward suffering rather than away from it. Jesus challenges religious authorities who use God to legitimize their own power. Jesus feeds people rather than lecturing them. Jesus welcomes the stranger. Jesus stands with those society declares expendable. And Jesus tells his followers that greatness consists not in domination but in liberation. That is a radically different theology of power.
Another Christian Patriotism
Christianity offers an alternative to nationalism that does not require Christians to abandon love of country, but it begins by refusing to worship their nation. It means loving one’s neighbors, including neighbors who have crossed a border. It means seeking peace rather than glorifying war. It means protecting human life rather than measuring success by military superiority. It means asking whether public resources are being used to ensure that every person has food, housing, healthcare, education, dignity, and a meaningful opportunity to flourish.
And it means remembering that the Bible’s central story is not the triumph of one nation over all others. It is the liberation of an oppressed people. It is the insistence that Pharaoh does not have the final word. That is why the question “What would Jesus do?” cannot be separated from the question raised by Florence Reece’s popular song written in 1931 in Harlan County, Kentucky, during the union organizing drive of the United Mine Workers: “Which side are you on?”
Christian faith does not ask us to look down from the Pentagon, the White House, or any other seat of power and decide which people deserve compassion. Instead, Jesus teaches us to love God, love your neighbor, love even your enemy — and recognize Christ in the people that those in power tell you to hate and fear.
When Christian nationalism asks its followers to choose between faith and the stranger, between military might and peacemaking, between national supremacy and human solidarity, Christians — including the Christians in the highest reaches of power — should ask a different question. Not “How can we make America powerful enough to win?” But: What would Jesus do?
The answer begins where the Gospel always has: feeding the hungry, welcoming the immigrant, freeing the oppressed, and telling the people at the bottom that God has not forgotten them. That is not a weak Christianity. It is Christianity’s most dangerous claim about power: The last shall be first. The mighty shall be brought down. And the kingdom of God belongs not to those who dominate, but to those who serve.
In response to a new European Union law, AI platforms are implementing new schemes for watermarking the content they generate. Anthropic recently disclosed its future Claude models will use SynthID-Text, an approach Google created and released as open source. It uses a secret key that subtly changes the process a model uses for choosing the next word in a sentence. Whereas a top next word choice might be “cloudy,” the key might change it to “overcast.” Anyone who knows the key can determine if it was generated by the platform using it.
New research shows that SynthID-Text can change not just word selection but also the tools a model invokes and the chances it will adhere to or disregard safety guardrails it has been trained to follow. The threat can become greater in the face of an adversarial prompt, in which an attacker attempts to cause a model to carry out a harmful action, such as revealing a password or other sensitive information. Instructions that normally wouldn’t be followed will, in some cases, be performed once the watermarking is deployed. The finding underscores the need for developers to thoroughly test how their LLMs and agents behave when watermarking is in place.
Changing safety behavior
“As compared to the same models without watermarking, it is definitely going to change their behavior, especially when we place it under adversarial conditions, or we make these models call tools when they’re powering an agent,” Andrea Siposova, an AI security researcher at Lasso Security, told Ars. “Watermarking is made to not be perceptible to a reader, but we know that when we are changing anything about what the model is generating, it is going to cause some tradeoffs, it’s going to show up somewhere.”
Hackers ripped down a Flock camera above a roadway, made a near-complete copy of the data stored inside it, and shared the files with 404 Media and WIRED, revealing in new detail how exactly Flock Safety’s cameras track the movements of both vehicles and people. The hackers say they are also publishing details on how they managed to obtain the software, in the hopes that other people may copy them.
The breach provides an unprecedented look inside a system that Flock has described as protected by on-device encryption. The hackers were able to copy the camera’s storage and recover an encryption key stored on the device, which unlocked videos of thousands of vehicle detections. The hackers shared the material with 404 Media and the transparency nonprofit Distributed Denial of Secrets, which shared the data with WIRED. 404 Media and WIRED then analyzed those files as part of a joint investigation.
While much of the automatic license plate reader’s most sensitive storage remained encrypted and inaccessible, the joint analysis of the recovered data shows that software running on the device explicitly detects people as well as vehicles, license plates, and bicycles. The camera can produce dozens of images of a single passing vehicle and, according to several weeks of recovered logs, generated more than a million images. Its computer-vision software also sometimes isolated bumper stickers and other graphics, including, in one case, an American flag patch on a motorcyclist’s saddlebag.
With doomsday AI scenarios dominating the news, lawmakers are rightly concerned about reports concerning security breaches at major US AI labs, such as the OpenAI–Hugging Face incident and the many others reported in its aftermath. As they consider potentially regulating frontier AI, they should focus any new legislation on the immediate, demonstrated risks from those incidents.
Post-incidentreports show that the Hugging Face incident could have been mitigated or prevented by following longstanding cybersecurity best practices, like stronger sandboxing and monitoring. Any new legislation should focus on closing gaps in existing law to prevent AI companies from taking unreasonable risks with the public's security.
When an AI developer or deployer runs a test or a task that has a high likelihood of causing harm to third parties—for instance, by breaking into someone else's computers—there should be clear minimum safety requirements. Such tests should run in a properly sandboxed test environment, disconnected from other systems, and be monitored and logged. Following these fundamental best practices would have prevented or substantially mitigated all of the incidents at AI labs that we currently know about.
That said, any proposal must be flexible enough to evolve with changing technology. Minimum safety requirements specific only to current AI technologies are likely to become obsolete; legal standards tied to well-established cybersecurity best practices are far more likely to stand the test of time. Tying any new mandates to evidence-backed security protocols also protects the public without impeding future AI development.
Strong legislation should also mandate and fund independent third-party investigations into any serious security incidents that may occur during AI labs’ tests of new tools, and make reports of these investigations available to the public. This important transparency measure would go a long way toward providing public oversight of the industry.
As with any technology regulation, those targeting cybersecurity practices at AI labs must be careful, precise, and practical.
The International Meteor Organization, the nonprofit that coordinates and publishes amateur and professional observations of meteor phenomena, said its infrastructure has suffered a “critical blow” from a cyberattack.
“We recently suffered a cyberattack that dealt a critical blow to aging infrastructure, taking much of our site offline," a static page on its website on Wednesday said. “We expect several weeks of partial downtime as we transition to new infrastructure and services.”
“I am very sad to see the site down”
In the meantime, the IMO said it’s prioritizing the reporting of fireball observations, which can be reported here. The organization is also providing some information on its Facebook page.
The U.S. military is straining under the pressures of the Iran war, according to two U.S. officials familiar with operations in the Middle East. One cautioned that this stress could lead to a “breakdown” in the military’s ability to effectively continue a war that President Donald Trump said would end in early April.
As the conflict has engulfed the region, the military has grappled with a growing list of challenges: Iranian attacks on U.S. bases and warships in the Middle East, depleted stockpiles of defensive munitions, increasing casualties, maintenance issues on ships, lengthy troop deployments, complicated logistics, flagging morale and a host of other issues that have taken a heavy toll on troops, damaged military readiness, and a strained Pentagon budget — contradicting months of rosy pronouncements by the Trump administration.
Both officials said that Iran is facing extreme economic pressure, according to intelligence reports. The first official characterized recent Iranian attacks on warships with ballistic missiles as a “go for broke” strategy to increase economic pressures on America ahead of the U.S. midterms. That official said it was unclear which country would “blink first.”
Trump suggested on Sunday that the U.S. could “stay and keep the oil” in Iran, like the neo-colonial resource grab the administration is carrying out in Venezuela. The second official said that a U.S. occupation of Iran would be “almost impossible” and that the idea was “nonsensical obviously.”
Iran’s ability to overwhelm U.S. air defenses in the Middle East using attack drones and advanced ballistic missiles, as previously reported by The Intercept, has left the U.S. military in a precarious state. The Trump administration failed to appreciate Iran’s military prowess, said the first official. The other pointed to a “complete lack of planning” for the war. Since July 7 alone, there have been hundreds of U.S. casualties caused by Iranian attacks, according to official Pentagon statistics.
The officials said the military’s ability to function at peak capacity was crippled in the opening hours of the conflict when an Iranian missile and drone attack on February 28 destroyed Navy facilities in Manama, Bahrain, the region’s most critical logistics hub. The Pentagon claimed for months that the strikes did not significantly impact military operations, but last week acting Navy Secretary Hung Cao admitted “they blew the hell out of Bahrain.” More than six months after the attack, Naval Support Activity Bahrain remains a shambles. “We’re not getting back in there anytime soon,” said Chief of Naval Operations Adm. Daryl Caudle, the Navy’s highest-ranking officer, during a recent town hall.
A Wall Street Journal investigation previously found that rebuilding the U.S. Navy’s Fifth Fleet headquarters, barracks, and communication towers at NSA Bahrain may cost more than $400 million, which the second official said could be an underestimate if it’s ever attempted. Naval Forces Central Command referred questions about the cost estimate to Central Command, which did not respond.
Trump has touted the destruction of Iran’s navy as one of his signature accomplishments of the war, but the officials pointed to the severe strain placed on U.S. naval forces in the region. With the home of the Fifth Fleet knocked out and other ports in the region within range of Iranian missiles and drones, the Navy found itself facing the daunting challenge of maintaining a flotilla of more than 24 ships — including two massive aircraft carriers and numerous guided-missile destroyers and cruisers, attack submarines, or supply ships deployed at any one time.
While aircraft carriers are nuclear-powered, the planes and helicopters on them, as well as the other ships, require millions of gallons of fuel each week. And the sailors aboard the ships require hundreds of thousands of meals. This means Navy ships need to haul supplies more than 2,000 miles from a longtime U.S. base on the Indian Ocean island of Diego Garcia. A War Department inspector general report released on Monday noted that the shift in “naval bases and support ports posed significant challenges,” pointing specifically to the “issue with shifting logistics support and infrastructure to Diego Garcia” and the challenges of “extended sea transit requiring 14- to 18-day logistics cycles.”
“It’s difficult and ultimately unsustainable,” said the second official, who told The Intercept that White House assumptions that Iran would “crack” before the Navy have yet to be borne out.
The Navy has just 11 aircraft carrier strike groups, and amid the ongoing strain of extended deployments, its oldest carrier, the USS Nimitz, has seen its service life extended. So far, four of the 11 carrier strike groups have already been deployed to the Middle East during the war. Some of the remaining carriers are undergoing substantial repairs and will not be ready to deploy again for years.
The USS Gerald R. Ford Carrier Strike Group completed a record-breaking, 11-month deployment that also included the invasion of Venezuela. (Under normal conditions, a carrier would visit port about once a month to allow its crew to rest.) The ship was, according to a Presidential Unit Citation, under “persistent threat from enemy missiles and one-way attack drones” during its deployment to the Middle East.
Early in the Iran war, the Ford suffered extensive damage from a laundry fire and a malfunctioning fire-suppression system that forced crew members to manually fight the blaze for around 30 hours. The fire halted sorties for two days, and around 600 sailors lost access to their bunks due to the damage. The Navy claimed few casualties from the blaze, but reports soon emerged that the more than 200 sailors were treated for smoke inhalation or lacerations.
The Ford has also been plagued by plumbing issues for years. During just a four-day span in 2025, there were 205 breakdowns. Before the Ford left the Caribbean, it was facing constant issues with the nearly 650 toilets aboard. And then in the Middle East, the carrier again suffered from clogged, excrement-filled toilets, according to video obtained by CNN.
Another carrier, the USS Abraham Lincoln, spent most of its nine months at sea with no port calls, leading to reports of rampant morale problems, supply shortages, and suicide attempts, with at least one crew member going overboard. At an August 11 town hall in San Diego, families expressed deep concerns about their loved ones to Cao, the acting Navy secretary. But Trump dismissed worries about the sailors, saying the Lincoln’s deployment was “not nearly long enough.” Last month, the Lincoln was relieved by the USS George Washington, allowing the heavily rusted Lincoln to pull into Thailand for a port call.
Those ships have left the region but sailors remain under persistent threat. The Islamic Revolutionary Guard Corps targeted a U.S. aircraft carrier and guided-missile destroyer with ballistic missiles this month, according to Central Command. CENTCOM did not reply to a request for additional information about the strikes.
Despite months of claims by Trump and self-styled War Secretary Pete Hegseth that Iran’s military was annihilated, Iran has attacked more than 15 bases across the Middle East, according to information from U.S. officials and Iranian reports.
Stocks of advanced air-defense missiles, like Patriot and THAAD interceptors, are so depleted that U.S. forces are not shooting down all Iranian missiles and drones aimed at U.S. and allied targets across the Middle East, according to U.S. officials who spoke to The Intercept as well as numerous press reports.
Trump and Hegseth have pushed back on these claims. Trump posted on Monday that the U.S. is “producing more Exquisite and Elite Weapons than at any time in our History,” but the aforementioned inspector general report immediately contradicted the president, revealing that the conflict has resulted in “strategic inventory shortfalls and revealed industrial base bottlenecks for munitions resupply.”
“I have all the munitions necessary to both defend our forces as well as conduct a broad range of contingencies,” Adm. Brad Cooper, the CENTCOM chief, told Congress in May. But even the Pentagon admits that 410 U.S. troops have been killed or wounded since July 7 alone. Three U.S. soldiers were killed during Iranian ballistic missile and drone attacks on Jordan’s Muwaffaq Salti Air Base on July 17 and 18, for example. And an Iranian drone attack on Erbil Air Base, Iraq, on July 18 killed one soldier and left another injured during what CENTCOM called a “controlled detonation” of the downed aircraft.
The U.S. and its allies burned through more than 11,000 munitions, including large amounts of defensive missiles, in the first 16 days of the war alone, according to a March analysis by the Royal United Services Institute. About 65 percent of Patriot interceptors were expended between February and July, leaving fewer than 830 remaining from a pre-war total of 2,330, according to an analysis by the Center for Strategic and International Studies. The number of THAADs dropped from more than 450 to less than 270.
On Sunday, Cooper, the CENTCOM commander, continued to downplay the risks of depleted stockpiles and told CBS’s “60 Minutes” that he wasn’t worried for the safety of U.S. troops. “I’m not concerned at all,” he replied when asked about defending against Iranian attacks. CENTCOM did not reply when asked if Cooper would resign if U.S. troops were killed or wounded in future attacks.
In addition to the destruction of NSA Bahrain, the Combined Air Operations Center at Al Udeid Air Base, Qatar, was severely damaged by Iranian missiles early in the war, rendering it inoperable. Both were recently attacked again, raising questions about whether either will ever be rebuilt. Iran also struck Muwaffaq Salti Air Base in Jordan last week, damaging multiple U.S. military aircraft, according to the second U.S. official. In response, U.S. forces fired a “significant” number of Patriot interceptors to protect U.S. forces, the second official said.
U.S. officials confirmed that Iran has also attacked Tower 22, a U.S. military outpost on the northern Jordanian border with Syria. Satellite images as well as photos and videos circulating online indicate the base suffered extensive damage. (In 2024, a drone attack on Tower 22 by an Iran-backed militia killed three U.S. troops.)
CENTCOM failed to respond to a request for comment about attacks on its outposts or provide its own official count of the number struck. But the Pentagon inspector general report revealed Iranian strikes “damaged and destroyed hundreds of buildings and structures at U.S. bases in Kuwait, Bahrain, Qatar, UAE, Saudi Arabia, Iraq, Oman, and Jordan during the conflict.” It also disclosed that “dozens of U.S. aircraft were destroyed or damaged,” including four F-15 fighter aircraft, 12 KC-135 refueling aircraft, and as many as 30 MQ-9 Reaper drones.
I can still remember the smell. But I’m at a loss to accurately describe it to you. It wasn’t the unmistakable odor of death, although that must have been some tiny part of it. It wasn’t like burning tires or plastic or even metal. It was all that, but it was more.
In the quarter century since, I’ve been all over the world, but I’ve never experienced anything like the smell near the rubble pile at Ground Zero in September 2001. The air was acrid and thick, a swirl of toxins and carcinogens made possible by turning two large, jet-fuel laden planes into cruise missiles and aiming them at gigantic office towers. As it burned, we all inhaled a haze of pulverized cement, glass fibers, asbestos, lead, dioxins, polycyclic aromatic hydrocarbons, polychlorinated biphenyls (better known as PCBs), and whatever else. It remains a part of us still.
The 9/11 attacks — which killed almost 3,000 Americans, toppled New York City’s Twin Towers, wrecked the Pentagon, and took down a plane near Shanksville, Pennsylvania — marked the most devastating intelligence failure in U.S. history and sent the United States into a paroxysm of self-induced catastrophes from which it has never emerged. Al Qaeda leader Osama bin Laden’s spectacular coordinated assault supercharged what had been a slow-motion imperial decline, trapping the U.S. in a death spiral of ruinous intertwined economic debacles, foreign policy failures, democratic backsliding, authoritarianism, and debilitating wars and military interventions.
Bin Laden’s plan was to trap the U.S. in expensive, foreign quagmire wars that would trigger a domestic economic collapse. It was patterned on the strategy that the local mujahideen, he and other foreign fighters, and the U.S. and its allies had used to defeat the Soviet Union in Afghanistan.
Not only does bin Laden’s strategy continue apace long after his 2011 death, but it also spawned an even more effective means of destroying America from within. Bin Laden’s attacks turned the U.S. government into an engine for the destruction of America, inducing it to implement policies that have devastated the country and immiserated its people. That includes unrestrained spending while cutting taxes on the rich, closer ties with despotic regimes, the sneak-and-peek warrants and roving wiretaps of the Patriot Act and other domestic surveillance programs, and the ruinous failed forever wars in Afghanistan, Iraq, and elsewhere.
This swirl of toxic policies and governmental overreach opened the door to something beyond bin Laden’s wildest dreams, the rise of an even more effective terrorist who has crippled the U.S. in countless ways and sought to strangle the best of the country: President Donald Trump.
Hijackers crashed planes into the Twin Towers at the World Trade Center on Sept. 11, 2001, in New York City. Photo: zz/Larry Le Vine/STAR MAX/IPx via AP Images
The so-called Pearl Harbor of the 21st century was no surprise. Long before President George W. Bush, while vacationing at his ranch in Crawford, Texas, received a classified intelligence memo titled “Bin Laden Determined to Strike in U.S,” the Al Qaeda leader had been honest about his plans. “The call to wage war against America was made because America has spear-headed the crusade against the Islamic nation,” he announced in a 1998 TV interview, castigating the U.S. for stationing troops in the Middle East and its support of Israel. “The Western regimes and the government of the United States of America bear the blame for what might happen. If their people do not wish to be harmed inside their very own countries, they should seek to elect governments that are truly representative of them and that can protect their interests.”
When bin Laden made good on his threats, slaughtering thousands on 9/11, he knew it was bound to trigger a response. One possibility was a measured law-enforcement action that would end with arrests and legitimate legal proceedings. The other was a president standing on a rubble pile, vowing revenge, a never-ending fruitless war against a tactic (terror), a secret torture gulag, a forever prison, and a kangaroo court. One would be ruinous for bin Laden. The other, an answer to his prayers.
Bin Laden’s masterstroke was to attack the U.S. after it had elected a lightweight nepo-baby president and a power-mad vice president who had cut his teeth in Richard Nixon’s criminal-packed White House. While he came to be an enemy of Donald Trump, it was Dick Cheney who paved the way for America’s current would-be tyrant, with the vice president’s relentless campaign to concentrate power in the White House, creating an imperial presidency predicated on the “unitary executive theory,” a misbegotten notion that the Constitution grants the president unrestrained authority over domestic and foreign policy, such as unilaterally removing government officials and waging wars.
“A lot of what needs to be done here will have to be done quietly, without any discussion.”
In both style and substance, Cheney prefigured Trump. In the immediate wake of 9/11, Cheney went on TV to announce the government would now operate on the “dark side,” as he put it, claiming “a lot of what needs to be done here will have to be done quietly, without any discussion.”
America has never emerged from those sinister shadows. Cheney was arguably the leading cheerleader for the ruinous war on terror, which began in Afghanistan, spread across the globe, and grinds on a year after his death; a prime architect of the disastrous Iraq War and the faulty, unverified, and cherry-picked intelligence that underpinned it; an enthusiastic supporter of torture, calling the waterboarding of detainees “a no-brainer”; a vocal supporter of domestic surveillance; a promoter of undemocratic, unprecedented, and unparalleled secrecy; and a belligerent bully.
“In our nation’s 246-year history, there has never been an individual who was a greater threat to our republic than Donald Trump,” Cheney said in a 2022 ad for his daughter, Liz, one of 10 House Republicans who voted to impeach Trump at the end of his first term. He might have been right — and he was certainly responsible. Trump has built on Cheney’s accomplishments and pushed America toward autocracy at an unprecedented rate.
Trump has built on Cheney’s accomplishments and pushed America toward autocracy at an unprecedented rate.
Bin Laden was never able to raise an army in America, lead an insurrection, and launch an attack on the U.S. Capitol. (The plane meant to carry out that attack on 9/11 crashed in rural Pennsylvania.) But on January 6, 2021, with Trump’s encouragement, MAGA supporters stormed the Capitol. The House Select Committee that investigated the “domestic terrorist attack upon the United States Capitol Complex and issues relating to the interference with the peaceful transfer of power” concluded that Trump engaged in a “multi-part conspiracy to overturn the lawful results of the 2020 Presidential election.” It found that Trump, for hours, deliberately failed to act to stop his followers from attacking the Capitol. Smith said that the evidence gathered by his team “was sufficient to obtain and sustain a conviction at trial,” had the American people not reelected Trump.
Bin Laden would have no doubt cheered the attack on the Capitol and endorsed Trump’s reelection run, had he been alive. And he would not have been disappointed by the results. Upon returning to office, Trump unleashed a coordinated assault on American democracy, undermining the rule of law and fundamental freedoms by pardoning and rewarding insurrectionists; weaponizing the Justice Department, regulatory agencies, and the military against American citizens; firing government watchdogs; attacking the free press; engaging in naked and unrestrained corruption, such as violating the Constitution’s emoluments clause; engaging in due process violations, immigration lawlessness, and unconstitutional executive power-grabs; and launching a disastrous war with Iran and a murder-spree on the high seas amid a host of other foreign and domestic policy fiascos.
Since January 2025, there have been nearly 4,000 separate authoritarian acts by the Trump administration including around 1,050 undermining democracy, more than 940 suppressing dissent, over 650 aggressive or destabilizing foreign policy efforts, about 600 acts weakening civil rights, around 500 centered around controlling information or spreading misinformation, and more than 320 acts of corruption, according to the Trump Action Tracker, which documents acts and statements of Trump and his administration that echo those of other authoritarian regimes.
A startling global analysis also discovered “autocratization” in America rose at a speed “unprecedented in modern history” last year. Under Trump, the researchers found, the U.S. has ceased to be a functioning liberal democracy after the largest one-year drop in democratic principles in American history. This took the country back to 1965 levels, when Jim Crow racial discrimination in voting — including violence and intimidation, poll taxes, and literacy tests — were still commonplace. These results are bolstered by research by the nonprofit group Protect Democracy, which finds that the corrupting of elections, quashing of dissent, spreading of disinformation, and aggrandizing of executive power are all “escalating” in Trump’s second term, while both authoritarian actions and the politicizing of independent institutions in the U.S. are “rapidly escalating.”
In 2001, the U.S. government recorded a budget surplus of about $128 billion and was projected to pay off the national debt by 2009. But after miring the U.S. in forever wars in Afghanistan, Iraq, Somalia, and elsewhere, bin Laden looked upon the fruits of 9/11 and took a victory lap in 2004, bragging that his strategy of “bleeding America to the point of bankruptcy” had helped to push the U.S. deficit to “more than a trillion dollars.”
“All that we have to do is to send two mujahidin to the furthest point east to raise a piece of cloth on which is written al-Qaida, in order to make the generals race there to cause America to suffer human, economic, and political losses without their achieving for it anything of note,” bin Laden announced.
He could not have imagined just how closely and how long America’s leaders would hue to his plan, conducting commando raids, drone strikes, armed interventions, and outright wars in Afghanistan, Central African Republic, Cameroon, Egypt, Iran, Iraq, Kenya, Lebanon, Libya, Mali, Niger, Pakistan, the Philippines, Somalia, Syria, Tunisia, Yemen, and elsewhere. Nor could Al Qaeda’s leader have foreseen how deep into financial ruin the U.S. would sink as a result.
Bin Laden’s 2004 trillion-dollar boast wasn’t actually accurate. The U.S. federal deficit was just $413 billion in 2004. But it wouldn’t remain that low for long. America’s post-9/11 wars have now cost or caused long-term obligations to taxpayers of an astonishing $8 trillion, according to a 2021 analysis by Brown University’s Costs of War Project.
And Trump has continued to expand America’s ruinous foreign interventions from Ecuador to Iran. An Intercept analysis found that Trump has presided over more than 20 armed conflicts and wars during his two terms in office. And the costs continue adding up. Linda Bilmes, a former assistant secretary and chief financial officer of the U.S. Department of Commerce and currently a public policy professor at the Harvard Kennedy School, previously told The Intercept that the excessive expenses of the Iran war, alone, would likely reach into the trillions of dollars. And Trump is also currently pushing for a post-World War II record $1.6 trillion Pentagon budget for next year.
“The Trillion Dollar War Machine,” by William D. Hartung and Ben FreemanAvailable at Bookshop.org.
In case you hadn’t guessed, the pre-9/11 projection that the national debt would be paid off in 2009 never came to pass. Instead, the Bush and Trump presidencies were marked by massive tax cuts that mostly benefited corporations and the wealthiest Americans, depriving the Treasury of almost $10 trillion in expected revenue.
So after bin Laden’s attack; the forever wars of Bush, Barack Obama, Trump, and Joe Biden; and Trump’s contributions in disastrous conflicts and gross fiscal mismanagement, the $5.8 trillion national debt of 2001 has now ballooned by 590 percent to a staggering $40 trillion. That’s $1 million, 40 million times over.
About 50 percent of the debt has been accrued since Donald Trump was first elected. This week, Trump pledged to pay every American adult $5,000 if Republicans keep control of Congress in November, which would cost more than $1 trillion. And that $128 billion budget surplus from 2001? It’s been replaced by a projected federal budget deficit for this fiscal year of $2.1 trillion. This debt and deficit spiral is also occurring during a time of near-full employment when the government’s finances should actually be improving.
If bin Laden made it to paradise, as was his hope, he is no doubt smiling as the Trump administration dismisses the ballooning debt and the president peddles nonsensical claims that “growth will take care of that very easily.” The U.S. will actually spend more than $1 trillion this year just paying interest on the debt. The Peterson Foundation projects that total interest payments will more than double over the next decade — and that may be an undercount. And even if the debt remained steady at $40 trillion and the United States were to pay down $1 million per day, it would take almost 110,000 years to pay it off.
All this debt is also likely to keep interest rates high, raising the cost of mortgages, auto loans, credit cards, and small business credit, hurting ordinary Americans. High deficits and debt — particularly if coupled with high inflation or interest rates — make it harder for the government to respond to crises like a recession, depression, pandemic, or other emergency.
Then there is the weakened safety net that comes from deficits and debt. Bin Laden doesn’t need to worry about his golden years, and Trump is living them right now at taxpayer expense. But in 2032 — just six years from now — the Social Security trust fund is on track to go bust, to take one example of shortfalls on the horizon. By law, when the trust fund hits zero, all retirees’ benefits are mandated to drop by more than 20 percent.
Looking back, I’ve come to think of the acrid odor of the collapsed Twin Towers as more than a mélange of burning paper, glass, concrete, and around 70 carcinogens. It was, instead, a harbinger of something even darker than the nearly 3,000 Americans who died on 9/11 — a long road of death and destruction stretching out into the future, beyond the vanishing point.
Even Bin Laden couldn’t have imagined long-term lethality of his attacks. Close to 9,700 first responders, survivors, and those who helped to clear nearly 1.8 million tons of debris at the World Trade Center have died of illnesses tied to 9/11, according to the September 11th Victim Compensation Fund. And more than 57,000 first responders and others have been diagnosed with 9/11-linked cancers. Around 155,000 people have enrolled in the World Trade Center Health Program, which provides care and health monitoring to people who were exposed to toxic air after 9/11. And an estimated 400,000 people were exposed to toxic contaminants, the risk of physical injury, and physically and emotionally stressful conditions in the days, weeks, and months following the attacks, according to the Centers for Disease Control and Prevention.
The vengeful war on the world that bin Laden managed to provoke has proved even more devastating than the effects of the toxic stew we inhaled near Ground Zero. An estimated 940,000 people were killed by direct post-9/11 war violence in Afghanistan, Iraq, Pakistan, Syria, Yemen, and elsewhere between 2001 and 2023, alone. Another 3.6 to 3.8 million people are estimated to have died indirectly in post-9/11 war zones, bringing the toll to at least 4.5 million dead and counting. This quarter century of carnage and all that it unleashed has left the U.S. hollowed out and rotting from within; a deterioration in every conceivable measure from economics to democratic ideals to the spiritual health of the nation.
Bin Laden’s bleed-until-bankruptcy plan was designed to sink America’s economy — and it continues to work to great effect. And by ushering in the presidencies of Donald Trump, bin Laden left the United States morally bankrupt, too. Twenty-five years after 9/11, the country is a pale shadow of the superpower that emerged from World War II having been laid low not by the Soviet Union — the nuclear-armed power it long considered an existential threat — but by two trust-fund terrorists: the scions of a Saudi construction empire, and an outer borough New York City real estate developer, respectively.
“The wise man doesn’t squander his security, wealth, and children for the sake of the liar in the White House,” bin Laden said in 2004, referring to Bush. He likely couldn’t have imagined America choosing an even more inveterate liar, an even greater intellectual lightweight, and an even more ruinous president. A quarter century after 9/11, it’s clear that bin Laden won. But the victory was not his alone. And, in the end, his role in it turned out to be vanishingly small. Bush, Cheney, Obama, and Biden, as well as a raft of politicians, government functionaries, and all who went along with the madness unleashed by the attacks, played key roles in helping hobble the U.S. in the 25 years since the September 11. But it’s been Trump, more than anyone else, who has made bin Laden’s lofty 9/11 dreams America’s never-ending nightmare.
Anthropic said it stopped multiple attempts by scientists this year to use its technology for research that could help develop biological weapons, as experts increasingly fear the threat that AI poses to public safety.
The startup gave five examples of times actors “circumvented controls” and made other efforts to “obfuscate” the purpose of their research to dodge safeguards. The cases involved some users in nations that it prohibits from accessing its models, which include Russia, China, and Iran.
“We hope that by sharing these examples, we spark a conversation within the AI industry and with governments about emerging biological risks and how best to counter them,” Anthropic said in a report about efforts to use its models for malicious activity.
It wasn’t that long ago that ClickFix attacks were exotic. Now the technique has become mainstream as attackers reap its simplicity and effectiveness in infecting users of PCs and Macs alike. All that’s required is a compromised website—a painless enough task—a fake CAPTCHA overlay, and the inclusion of a single terminal command. So many visitors get suckered into pasting and running the command that just about every malware pusher has adopted the technique. Even Kremlin-backed hacking groups are joining in.
“Reddit is becoming post after post after post of people getting their computer infected via ClickFix,” independent researcher Kevin Beaumont observed Thursday. “Legit websites everywhere [are] getting hacked to serve the fake captcha prompts.”
How many of us make things worse
More seasoned Internet users—a fair number who read this site—are quick to dismiss the attack. They typically blame the people who fall for the scams and marvel at their gullibility and lack of attention. The reality is that for more casual users, using computers and the Internet has become so difficult—think impossible-to-close interstitials, CAPTCHAs with an endless series of pictures to analyze, and constantly changing interfaces that bury the features they’re looking for—that they have grown desensitized to instructions that seem ridiculous and burdensome.
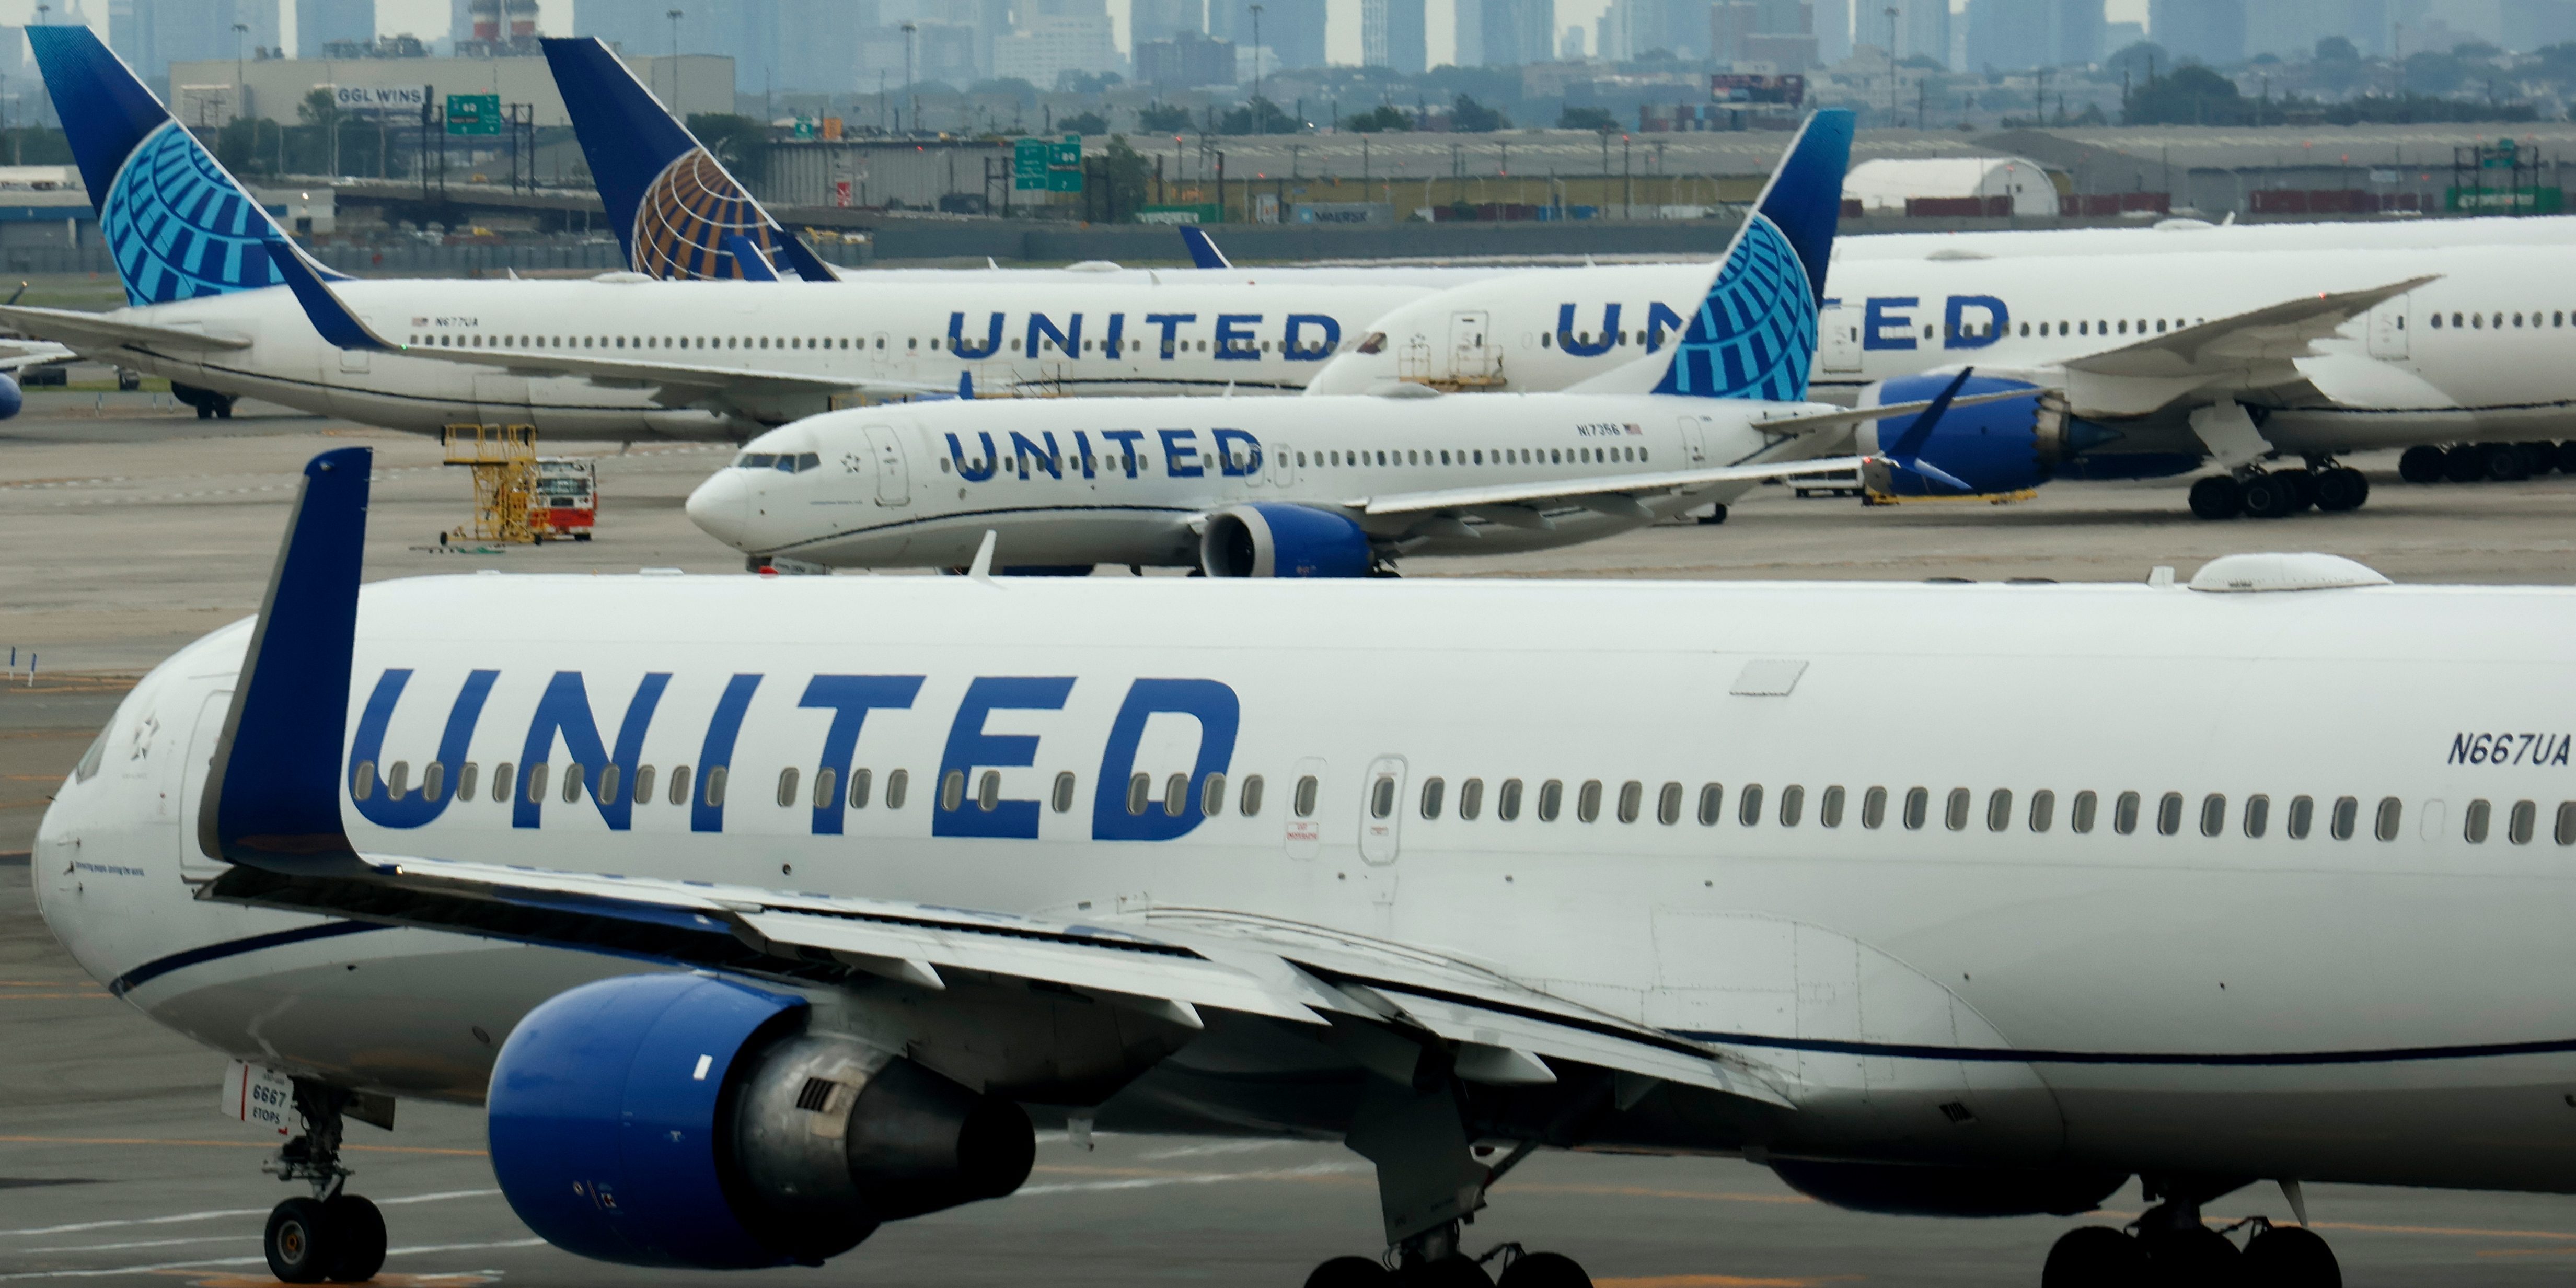
United Airlines is set to resume the shipment of military hardware to Israel aboard passenger flights, according to shipping data reviewed by The Intercept. The airline, one of the biggest in the world, had halted the practice more than six months ago amid the outbreak of the war on Iran.
On Wednesday evening, United is scheduled to transport five shipments of military cargo onboard United Airlines flight 90, a passenger route from Newark Liberty International Airport, in New Jersey, to Tel Aviv, Israel, a day after resuming the route and another direct flight to Israel, records show.
The shipments, according to documents reviewed by The Intercept, include one transport to the “electro-optics” wing of the Israeli weapons giant Elbit Systems, in Rehovot, Israel, where the arms maker has a major campus. Another shipment is bound for Elbit Systems Land, a division of the company formerly known as IMI Systems, located in Ramat Hasharon, Israel. And a further three shipments are scheduled to go to an Elbit Systems facility in Karmiel, Israel.
At least one of the shipments to Karmiel was specifically labeled as “FMS,” or foreign military sales, the records show, though all the military hardware bound for Israel on the Wednesday flight is destined for defense firms under Elbit’s umbrella.
“United, consistently and on a regular basis, ships military materiel that is used by the Israeli military.”
The shipments appear to be a return to status quo for United, which had used civilian passenger flights to transport thousands of shipments of military cargo to Israel amid its wars in the occupied Gaza Strip and Lebanon and in the run-up to its joint attack on Iran alongside the U.S., according to a new report released this week by Movement Research Unit, Palestinian Youth Movement, People’s Embargo for Palestine, and the Democratic Socialists of America. (A spokesperson for United declined to comment. Representatives of Lockheed Martin, Elbit Systems, and the Israeli Ministry of Defense did not respond to requests for comment.)
The report, based on open-source data, found that United transported nearly 3,000 loads of military materiel over a seven-month period in 2025 and early 2026. The cargo ranged from critical components for fighter jets and tanks to helmet displays, electronics, and nuts and bolts. The transfers stopped only amid the outbreak of war with Iran.
“This report shows that United, consistently and on a regular basis, ships military materiel that is used by the Israeli military for its operations in Gaza, in Lebanon, and against Iran,” said Griffin Mahon, a co-chair of the national labor committee of the Democratic Socialists of America, one of the groups behind the report. “These parts are shipped on civilian passenger flights, and they represent one way that American companies enable the Israeli government’s war crimes.”
2,761 Shipments
Using open-source methods to find publicly accessible cargo documents, researchers with the Movement Research Unit — a group that provides investigative muscle for left-wing groups and causes — said they tracked 2,761 shipments to weapons manufacturers transported by United aboard 160 civilian passenger flights between July 24, 2025, and February 27, 2026.
Due to the volume of data, the authors were only able to analyze a subset of the overall shipments, but after analyzing the product descriptions of a sample of 546 of those shipments, the group found 28 shipments of tank parts, 131 shipments of parts for weapons maker Lockheed Martin’s F-35 fighter jets, 67 shipments of components for other aircraft, and more than 100 other shipments of radio and communications equipment, nuts and bolts, and helmet-mounted display systems.
Many of those parts include key components to some of the most critical military vehicles in Israel’s arsenal, many of which have been documented in the commission of alleged war crimes on numerous occasions, according to Belal Elsiesy, a spokesperson for Palestinian Youth Movement.
“We’ve seen parts directly tied to the carrying out of the genocide, from armored tank sights and gunner display units to the bomb-release units of the F-35,” Elsiesy said. “We often have seen videos of Israeli occupation forces on social media recordings from inside of a tank, the demolition of schools, mosques, and other buildings, and often the screen that they are recording on is a gunner display unit — the same gunner display unit that is transported by United Airlines. It’s not an abstract connection.”
The report found no evidence that United transported any explicitly hazardous material aboard passenger flights. The use of civilian infrastructure to carry weapons components to a belligerent in the midst of open conflict, however, raised ethical questions for the researchers, according to Abdullah, an investigator with Movement Research who spoke with The Intercept on the condition that he be referred to by his first name only due to the sensitive nature of his work.
“There are ammunition handling systems and F-35 parts and tank sites that are being transported on these flights, without [passengers] actually knowing.”
“We all get on our flights and have to worry about taking too much water in our water bottles, and meanwhile, there are ammunition handling systems and F-35 parts and tank sites that are being transported on these flights, without us actually knowing,” Abdullah said. “Crimes are being committed in Gaza, so United needs to do a full and thorough review of their policy related to the transport of these components that might be violating international law.”
Weapons Parts on Domestic Flights
The cargo shipments were not just stowed away on flights bound for Israel, the report found.
While the majority of cargo documents for shipments did not reveal a domestic origin point other than Newark, 235 shipments were shown to have arrived at Newark on domestic flights from cities across the U.S., including flights from Dallas–Fort Worth International Airport, Houston International Airport, Atlanta International Airport, San Francisco International Airport, Los Angeles International Airport, along with Washington’s Dulles International Airport and Chicago O’Hare International Airport.
The domestic route with the most shipments in the period analyzed was a United flight from Dallas–Fort Worth to Houston, aboard which the airline transported 128 shipments, according to the report. That was followed by 90 domestic shipments onboard a United flight from Houston to Newark.
Most of the shipments going directly to Israel — 2,565 in total — appear to have been carried aboard United flights 84 and 90, passenger flights that travel directly from Newark to Tel Aviv. Data obtained by the report’s authors showed that Newark served as the primary hub for United’s shipments to Israel, with all but 45 of the shipments in the documented period arriving in Israel from there. Of the remaining 45 shipments, 36 left the U.S. from Chicago, and nine from Washington, the report found.
Most of the shipments — 2,070 in total — were destined for Elbit Systems, Israel’s largest weapons manufacturer and a frequent target of Palestine solidarity activism, according to the report. A total of 78 shipments were transported to the Israeli headquarters of Lockheed Martin, while hundreds more were destined for the Israeli Ministry of Defense and to several military airbases in Israel, including the operational hub of the country’s fleet of F-35I jets, the Israeli version of Lockheed’s flagship stealth fighter, the report found.
While information on the senders of the shipments was only available in some cases, a portion of the transfers were shipped by Lockheed Martin and by Elbit System’s U.S. branch, according to the report’s authors.
A New Report
The Intercept reviewed a portion of the underlying data in the report, including cargo documents that showed the transport of F-35 parts and weapons systems for armored personnel carriers, but has not independently corroborated every claim made by Movement Research Unit and its partners.
Movement Research investigators provided a detailed explanation of its methodology to The Intercept, which agreed to withhold some details to prevent a clampdown on the research that made the report possible. Previous work by the group has exposed a multi-ton shipment of explosive material out of New York’s John F. Kennedy International Airport and a Portland drone company shipping hardware to Israel.
Work on the report began last summer, after an investigative story by the Irish publication The Ditch revealed several shipments of military hardware aboard passenger flights passing through Irish airspace.
Suspecting the practice might be more widespread than the limited samples in The Ditch report, Movement Research delved deeper into the airline’s shipments to Israel over the ensuing seven months.
The shipments appear to have mostly stopped in February, when U.S. direct flights to Israel were suspended amid the U.S.–Israeli attack on Iran. With those flights set to resume this week, the report’s authors hope to pressure United to cease its practice of moving military cargo onboard, according to Abdullah, the investigator with Movement Research.
“This is very timely, because United needs to commit to not shipping military cargo on those passenger flights,” Abdullah said. “Not only on the ones that are going directly to Tel Aviv, but also on flights within the U.S.”
A nearly identical exploit kit that targets critical vulnerabilities in both Chromium-based browsers and older versions of Windows is being actively used by at least four hacking groups, some of which have ties to the Chinese government.
Researchers from security firm Proofpoint said Wednesday that BlueMoon, the name they gave to the kit, chains three vulnerabilities together so the attackers using it can install malware of their choice. BlueMoon exploits two Chromium vulnerabilities and one in the kernel of Windows 10 (Oct. 2018 Update), Windows Server 2019, Windows 10 2004, Windows Server 2022, and the initial release of Windows 11. All three vulnerabilities have received patches in the past 24 hours.
Deployed rapidly, widely shared
The attacks lacked the stealth found in many campaigns. More often, hackers want to exploit newly discovered vulnerabilities sparingly to lengthen their longevity. Proofpoint hypothesized that one reason for the widely used and visible exploit chain was to take advantage of a “patch gap” in the Chromium supply chain, which spans the time a patch is available from developers and the time that patch is incorporated into browsers such as Chrome and Edge. Another likely contributor was the use of AI, which can often spot vulnerabilities faster than discovery performed solely by humans.
The term “digital sovereignty” has become ubiquitous. European officials invoke it in debates about cloud infrastructure, AI, semiconductors, and platform regulation. Governments throughout the global majority use it to argue for greater control over data and communications infrastructure and boost their economies. Companies market “sovereign cloud” products designed to reassure their customers that their information stays under local jurisdiction. But digital sovereignty could be something more: an opportunity for users around the world to build more resilient, open systems and the skills and infrastructure to maintain them.
There is no singular definition of digital sovereignty, nor is there a single coherent position in the digital rights space. Despite its growing popularity, the term remains frustratingly vague. Policymakers, regulators, civil society groups, and others can mean very different things when they use the term. But to start simply with a broad definition, we can say that it means having the capacity to control one’s digital destiny—though the implications of that will obviously differ considerably whether you’re talking about an individual or a country.
We can start by developing a shared understanding of what digital sovereignty actually means. We’ve also included a glossary of terms at the bottom of this post.
In Europe and other places where digital sovereignty has become a topic of policy, discussions focus on reducing dependency: on foreign (and particularly American) cloud infrastructure, chips, platforms, and at times, foreign political priorities. The concern is both economic and geopolitical. If essential infrastructure is controlled by companies elsewhere—and thus subject to the laws of another jurisdiction—then what control does a country actually have over its own digital future?
In global majority countries in particular, wars, sanctions, and the growing fragmentation of the internet have demonstrated for many that the physical infrastructure that underlies digital life is neither neutral nor invulnerable.
Amidst this increasing geopolitical instability governments and civil society should consider whether digital sovereignty can help shore up that infrastructure.
What are we talking about when we talk about digital sovereignty?
A recent Franco-German joint paper on digital sovereignty defines it as the “capability and capacity to develop, provide, use, adapt and control digital technologies including hardware in an independent, self-determined and secure manner” and puts forward a framework to operationalize Europe’s capacity to act in the digital domain.
Some governments, such as Germany’s, have started to put funding behind sovereignty efforts through initiatives like the Sovereign Tech Agency, which “invest[s] globally in the open software components that underpin Germany's and Europe's competitiveness and ability to innovate.”
Positions on digital sovereignty among EFF’s allies across Europe vary.Open Rights Group have defined digital sovereignty as “the ability of a country to have control over its digital infrastructure, data, and technology” and states it to be “critical for the UK’s economic and national security.”
Similarly, the European Partnership for Democracy hasexpressed concern that “a few Big Tech corporations decide our collective destiny,” and argue that the EU should explore “alternative ownership models for tech companies and clearly [define] their purpose and mission.” And our friends atEDRi (of which EFF is a member) havestated clearly that “Europe’s digital sovereignty starts with open source.” Some initiatives, such as DI.DAY, consider digital sovereignty an opportunity to free users from Big Tech dependencies.
Elsewhere in the world, conversations about digital sovereignty often take a different shape. Indigenousdiscussions of the topic have been ongoing for more than a decade and focus on the inherent right of Native nations to govern their own digital ecosystems. In Southeast Asia, the desire for digital sovereignty has created growth in the sovereign cloud industry, but the conversation isn’t purely economic: Concerns about jurisdiction for where data is held are driving much of the conversation.
In Latin America,digital public infrastructure is often a key aspect of debates. Across Africa, leaders speak of a desire to shift the continent from being consumers of technology to becoming architects of their own digital infrastructure and data ecosystems. And in the Middle East and North Africa, concerns about reliance on U.S. technology companies—which have engaged in conflict and disproportionate censorship (particularly of Palestinian voices) in the region—are often paramount.
Reem Almasri, a senior researcher based in Jordan, recentlyspoke to EFF about digital sovereignty, which she sees as “the ability of people and communities to choose, control, and use technology that serves their needs and values,” particularly in light of the role that U.S. companies have played in regional conflicts.
In a Januaryarticle, Almasri pointed to growing concerns about granting greater sovereignty and influence to governments over citizens’ data, communications, and websites, writing: “This is particularly worrisome in countries that impose high levels of internet and media censorship and run unaccountable surveillance programs on their citizens’ data.”
Indeed, while pushing for greater sovereignty from Big Tech has benefits, there is an inherent risk that some states will pursue digital sovereignty as a means of cutting off or splintering access—as we’ve already seen in Iran, Russia, and elsewhere.
For that reason, it’s no surprise that some, such as Iranian professor Azadeh Akbari,believe that “the current wave pushing digital sovereignty as the key to ending dependency on American and Chinese technology is negligent of its Eurocentric bias.”
What does EFF believe?
In a world where people have digital sovereignty, civil society should be able to communicate freely, privately, and anonymously if they wish. People should be able to easily understand where their data lives and who has access to it. That data should be easily portable between platforms and services.
At EFF, we view digital sovereignty not as a walled garden, but as an opportunity for resilience and development of industries and skills. We believe that governments can and should take a role in crafting digital sovereignty that centers the autonomy of users rather than just re-creating a state of digital dependency with a new set of companies. Governments should support and use free and open source tools and projects built using principles of interoperability and data portability. This support should include employing full-time developers, UX designers, and community managers. Government policy and legislation should grant users control of their own data and a clear understanding of who can lawfully access it. Digital sovereignty should foster users’ ability to choose how they use digital products and services, free from unfair lock-ins, coercive terms and manipulative defaults. It should also foster the broader public interest internet, the part of the web that provides public goods and useful services without requiring the scale or the business practices of the tech giants.
Encryption backdoors are fundamentally incompatible with a vision of data sovereignty that centers user control. Governments should support the development and normalization of reputable end-to-end encrypted communications as well as strong encryption for data at rest. This support should include employing cryptographers and contributing to strong, peer-reviewed encryption standards strengthened by data minimization as a fundamental design principle, as well as refraining from legislating mandates for “lawful access” or any other reason.
As technologists, we don’t have to wait for governments to act in order to create the digital sovereignty we want. We get the internet that we build. We can contribute to open source, decentralized, and end-to-end encrypted projects. We can build standards that make interoperability and data portability a feature from the very beginning. We can resist the call of proprietary solutions, user lock-in, and encryption backdoors.
And finally, while digital sovereignty is often framed as a response to the dominance of Big Tech, that does not mean that there is no role for private companies to play. There is no point in replacing the influence of a few mostly US-based tech companies with a handful of giants based elsewhere. Companies can and should build platforms and services on top of open source, decentralized protocols and contribute to the ecosystem. Companies should also minimize processing a person’s data except as strictly necessary to provide them what they asked for, and only with opt-in consent that makes it clear to users what data they are gathering, where it is stored, and who has access to it. And companies should build their tools and platforms in a way that allows interoperability and that makes it easy for users to leave with their data. Some of these practices are already required by law in some jurisdictions, but companies don’t have to merely do the bare minimum the law demands: they should respect their users and support data sovereignty right now.
A glossary of terms
The following terms are useful for understanding this blog post as well as the broader conversation about Digital Sovereignty:
Intermediary liability: the legal responsibility of online service providers (ISPs, websites, social media platforms) for unlawful activities by their users, such as defamation, copyright infringement, or illegal hate speech.
The stack: a secure, open-source technology framework, often focusing on European alternatives, designed to break dependencies on (mostly) US-based technology providers. It comprises interoperable, vendor-neutral, and transparent digital infrastructures designed to regain control over data, infrastructure, and technology.
Digital sovereignty: the ability of people, as nations, organizations, and individuals, to control their own digital destiny by retaining authority over their own data, technology, and infrastructure.
Data sovereignty: the principle that digital information is subject to the laws and governance frameworks of the country or region where it is physically collected, stored, or processed. It dictates that data remains bound by the specific privacy protections and regulations of its originating jurisdiction, regardless of where the collecting organization is located.
Digital commons: a shared, online resource, such as knowledge, software, and data, that is collectively produced, governed, and maintained by a community, intended for public access. Examples include Wikipedia, open source operating systems such as Linux, and Creative Commons licensed content.
Data portability/interoperability: the ability to easily transfer personal data from one service provider to another, or to a personal system, in a structured, machine-readable format. It empowers users to move away from "walled gardens," reducing vendor lock-in and enhancing user autonomy.
Digital dependency: the opposite of digital sovereignty. The inability of people as nations, organizations, and individuals to control their own digital destiny through control over their own data, technology, and infrastructure.
Decentralization: a shift away from relying on centralized, often US-based, corporate platforms toward a distributed, user-centric internet where individuals, communities, and nations maintain control over their data, digital identity, and infrastructure.
End-to-end encryption (e2ee): a secure communication process where only the sender and intended recipient can access, read, or decrypt messages or data.
Fairness (à la the Digital Fairness Act): the absence of deceptive, manipulative, or addictive design practices that distort consumer choice and exploit vulnerabilities.
User sovereignty: the concept that individuals possess absolute control over their personal data, digital identity, and online privacy, rejecting the centralization of power by large technology platforms. It emphasizes user consent, decentralization, and the ability to manage personal data using secure and independent tools.
The Department of Defense asked OpenAI to provide the U.S. military with a special version of its artificial intelligence technology designed to turn down the military commands as infrequently as possible, according to documents obtained by The Intercept.
The desire for a custom AI tool with “minimal refusal rates” to Pentagon commands was revealed in files released to The Intercept as part of a Freedom of Information Act lawsuit seeking information about the military’s secretive deals with AI companies.
OpenAI, along with rivals Google, xAI, and Anthropic, all agreed in 2025 to develop militarized prototypes of their state-of-the-art AI to assist the armed forces in uses including logistics, intelligence decision-making, and general “warfighting.” Earlier this year, the Pentagon sought to expand the scope of these agreements and deploy them across U.S. classified computer networks, resulting in a high-profile showdown with Anthropic over whether and how the company could restrain military uses of its technology.
The clause seeking “minimal refusal rates” from OpenAI appears in an updated contract — version “P00003” — expanding upon last summer’s prototype deal, worth up to $200 million over the contract’s two-year duration. A separate document, signed by both OpenAI and the government on February 6, indicates that OpenAI agreed on that day to the contents of an expanded version “P00003.”
OpenAI and the Pentagon deny agreeing to such “minimal refusal ” language, claiming that the “P00003” document provided to The Intercept was a draft and not the final version. “OpenAI has never agreed to contract language requiring ‘minimal refusal rates.’ This language does not appear in our executed contract,” said spokesperson Nate Evans.
“The document you received appears to be an earlier draft proposed by the Department before we provided feedback. We rejected that language, the department agreed to remove it, and the final executed agreement does not include it,” Evans said.
A screenshot of a heavily redacted Department of Defense document indicating the military’s desire for a version of OpenAI’s technology with “minimal refusal rates,” yellow highlight added.Document: Department of Defense
Working with Legal Advocates for Safe Science and Technology, The Intercept’s FOIA inquiry specifically sought only final, executed contract documents. The request asked the Pentagon to exclude any draft materials. None of the documents released through the lawsuit is marked as a draft.
When asked to confirm whether the document containing the “minimal refusal rates” clause was in the final agreement, a Department of Justice attorney representing the Pentagon in the lawsuit said it was indeed the signed and executed version of the contract.
Hours later, and following The Intercept’s outreach to OpenAI, however, the Pentagon’s lawyer said to disregard the prior confirmation, stating that the Department of Defense required more time to investigate the matter.
The Intercept was then contacted by Trevor Tiedeman, a special assistant to the under secretary of war for research and engineering, who prior to his Pentagon position worked for President Donald Trump’s reelection campaign. “There might be some stray voltage or wires crossing between whatever FOIA information you may have received versus what actually exists versus what is an executed contract per se,” Tiedeman said in an interview.
He suggested the document containing the “minimal refusal rates” clause may have been a draft copy, but said he was unsure of exactly what the document was, why it was produced to The Intercept pursuant to its FOIA request and lawsuit, or why the Department of Defense abruptly reversed course.
Tiedeman told The Intercept he would provide a full accounting of how the document was erroneously flagged by Pentagon FOIA officers, cleared for release by the Department of Defense, and then confirmed as accurate by the Pentagon’s lawyers. When asked if the Pentagon could share the correct version of the OpenAI contract it ostensibly neglected to release, Tiedeman said he would investigate the matter. He then stopped responding to The Intercept’s inquiries.
OpenAI similarly did not provide the full contract. (In 2024, The Intercept sued OpenAI in federal court over the company’s use of copyrighted articles to train its chatbot ChatGPT. The case is ongoing.)
Days later, the Justice Department lawyer representing the Pentagon further backtracked, stating the document in question “was not the final version of that document,” and that the “correct document” would be shared later, “although I do not have a definitive timeline.”
Department of Defense spokesperson Jacob Bliss later said in a statement “the phrase ‘minimal refusal rates’ does not appear in any active Department of War contract with OpenAI.”
The language indicating the military sought a more pliable version of OpenAI’s technology is found in a section of a contract document describing what OpenAI was obligated to deliver to the Pentagon. These deliverables included “Testing, Evaluation, and Refinement of OpenAI Mission Models” for “national security problem sets.” The document explains “’OpenAI Mission Models’ refer to OpenAI models that are designed for national security use cases and have minimal refusal rates.”
There is no indication in the paperwork about what these “national security problem sets” may entail. Nor is there any description about the kinds of requests the Pentagon hoped OpenAI’s technology would minimally refuse. However, a large language model that would aid in the process of spying on, targeting, and killing people would require a substantial relaxation of safeguards to be useful for any military.
Like many of its rival platforms, OpenAI’s flagship LLMs contain built-in guardrails that direct the tool to reject certain queries, typically on the basis of safety. Asking the consumer version of ChatGPT for help prioritizing drone-based airstrike targets, for example, generates this reply: “I can’t provide a prioritization scheme for conducting UAV airstrikes against specific enemy combatants.” OpenAI and its competitors ban the public from using their models for other dangerous applications, like the development of weapons of mass destruction.
Heidy Khlaaf, chief scientist at the AI Now Institute and former systems safety engineer at OpenAI, told The Intercept the notion of national security-specific guardrails is in itself worrying. “Minimal refusal is likely referring to little or no safeguards on the model being used,” Khlaaf said.
“Minimal refusal is likely referring to little or no safeguards on the model being used.”
No matter the final contract language, experts like Khlaaf are concerned about the role corporate policy is already playing in combat. “It is a worrying development that private corporations are given the power to [make] determinations in warfare that are ultimately state obligations, whether it be for targeting recommendations, or the guardrails deployed to constrain a state’s military use.”
Questions of what limits — if any — tech firms can or should place on battlefield usage were at the center of this year’s public brawl between the Pentagon and Anthropic. The company claims its military deal to expand into classified networks collapsed when the Defense Department refused to place contractual prohibitions against the use of its technology for autonomous weapon systems and domestic surveillance. The Trump administration in turn designated Anthropic a supply-chain risk and moved to ban it from government use (the designation was overturned late last month by a federal judge).
Such tensions didn’t stop OpenAI from quickly cementing its version of the deal. On February 27, OpenAI signed the latest iteration of its Pentagon agreement, permitting the use of its services across the U.S. military’s classified networks. The classified deployment contract update includes the same “Testing, Evaluation, and Refinement of OpenAI Mission Models” header, but its text, unlike the previous version, is redacted entirely.
OpenAI claimed that it secured red lines on autonomous killings and spying against Americans. But the way the deal is drafted ultimately allows for any uses the government deems legal.
The acrimonious breakup between Anthropic and the Department of Defense played out largely in public. But despite the high-profile salvos between the artificial intelligence giant and the Pentagon, ostensibly over the ethics of 21st-century warfare and corporate power, their actual falling out hinged on a government contract that has remained hidden away. Through a Freedom of Information Act lawsuit conducted with the help of Legal Advocates for Safe Science and Technology, The Intercept obtained more than 400 pages of documents related to the U.S. military’s contracts with Anthropic and its chief competitors. They illuminate the surprisingly intimate relationship between Big Tech and the armed forces, and reveal new insights about the deals that led to the Anthropic crisis earlier this year.
The documents, many heavily redacted, consist of contract paperwork from deals originally signed in July 2025 between the Department of Defense and Anthropic, Google, OpenAI, and xAI, as well as later amendments to those agreements. Through the contracts, each worth up to $200 million, the companies agreed to build prototypes of artificial intelligence tools to “improve military advantage, military utility, or enhance military decision making” across the whole of the armed forces. These prototypes, aimed at applications from “warfighting” and automated decision-making to logistics and military intelligence, would go on to form the basis of the artificial intelligence tools now deployed across the Department of Defense’s classified networks. The document set includes one contract reflecting OpenAI’s classified network deployment; The Intercept is awaiting the government’s production of equivalent documents from the other contractors.
The contract materials show the close and complex partnership between the Pentagon and the AI industry, and detail the extent to which AI firms themselves are expected to influence how their technology is used to augment the U.S. capacity to wage war.
“This appears to be the first time the extent of collaboration between frontier AI labs and the Pentagon is spelled out in explicit terms,” Sophia Goodfriend, a University of Cambridge research fellow and non-resident fellow at the Harvard Kennedy School’s Middle East Initiative studying the impact of big data and machine learning on military conflict, told The Intercept. “What’s particularly notable is the terms by which engineers are working in lockstep with the department of war to engineer AI systems for surveillance, targeting, and killing.”
Official announcements following the 2025 deals were light on details and heavy on platitudes. “We must equip our warfighters with 21st-century technology in order to defeat 21st-century threats,” explained Pentagon spokesperson Sean Parnell at the time.
Google was similarly cagey: “These advanced AI solutions will enable the DoD to effectively address defense challenges and scale the adoption of agentic AI across enterprise systems to drive innovation and efficiency with agile, proven technology,” the company said.
“What’s particularly notable is the terms by which engineers are working in lockstep with the department of war to engineer AI systems for surveillance, targeting, and killing.”
The contract documents for the prototyping project paint a clearer picture, revealing deals that involve far more than a simple sale of software.
An “information sharing” provision in all four agreements, for instance, creates a two-way exchange of data and expertise. The companies agreed not only to provide access to their best large language models, but also to “inform DOD and CDAO [Chief Digital and Artificial Intelligence Office] strategy on frontier AI and AI,” as phrased in the agreement with Google.
Under the agreements, the AI labs were approved to receive an array of sensitive information, which could include “benchmarks datasets for DoD use cases, appropriate briefings on DoD operational missions and threats to inform development / release of technologies, their application to DoD operational problems, or DoD plans and strategies for future AI adoption.”
All four companies would in turn provide the Pentagon “feedback on DoD strategies for frontier AI adoption to ensure that AI capabilities can be delivered and scaled to meet the warfighter’s needs.” The companies also pledged to offer briefings on corporate inner workings, including “frontier AI model performance, case studies on current or likely future frontier AI applications, or projections of future trends in frontier AI maturation.”
The labs would sometimes be the ones offering intelligence briefings on foreign actors, with Google tapped to inform the Pentagon on “AI tactics and techniques of adversaries” of the United States. These briefings would be conducted in both unclassified and classified settings.
The collaboration also entails Big Tech providing training and educational seminars directly to the military, including “Presentations and briefings at technical exchange meetings on relevant topics, including frontier AI model performance and case studies of frontier AI applications.” One document notes that Google, for example, would lead multiple seminars on “responsible AI” deployment.” The documents state engineers and policy experts from all four contractors will conduct “tabletop exercises,” gamified simulations of real-world scenarios, with the Pentagon.
This back and forth between the military and private sector would, the Pentagon hoped, allow for “iterative refinement of frontier AI models to address real-world challenges in areas such as intelligence analysis, cybersecurity, and autonomous systems,” according to contract language with all four companies.
The AI companies were contractually scheduled to provide “risk forecasting, and threat ideation exercises” — predictions of pitfalls and dangers their own products might pose in the future. “Frontier AI labs have advanced risk forecasting tradecraft and a clear vision of the next wave of frontier AI technological developments,” the contracts read. “Frontier AI companies can help DoD gain a better understanding of the risks that might be associated with subsequent near-term frontier AI models or features, to avoid strategic surprise and to mitigate the associated risks.”
Heidy Khlaaf, chief scientist at the AI Now Institute and former safety engineer at OpenAI, told The Intercept this is a dubious claim with dangerous implications. Pointing to recent disclosures by OpenAI and Anthropic that semi-autonomous large language models broke into computer networks owned by other companies during testing, Khlaaf questioned their fitness to help build guardrails in the first place. “This is a very concerning development,” she said.
According to Khlaaf, the “risk forecasts” so far offered by frontier AI labs have been light on evidence and tend to “emphasize self-beneficial skewed risks such as a purported AI arms race and speculative ‘existential’ risks,” like self-aggrandizing science fiction-style “Terminator” scenarios.
Trusting companies to self-report the risks of their own products constitutes a conflict of interest and a “subversion of democratic processes.”
The public would be better served, she said, with a reliance on independent assessment of the risks these companies present, not the word of the companies themselves. Trusting companies to self-report the risks of their own products constitutes both a conflict of interest, Khlaaf added, and a “subversion of democratic processes when AI labs are allowed to take over the arbitration of risk determinations with life-or-death consequences.”
As the prototyping effort progressed, the contract documents show the scope of the project expanded. New versions of the contract show additional deliverables included in the list of what the Pentagon was purchasing. The government redacted descriptions of these new deliverables on the basis of military secrecy and corporate confidentiality.
It was during the negotiation of these subsequent amendments when Anthropic and the Pentagon had their falling out. Anthropic refused to sign a follow-up deal to allow deployment of its technology on classified military networks without contractual prohibitions against use for domestic spying and autonomous weapons, leading Secretary of Defense Pete Hegseth to designate the firm a “supply chain risk” in March and ban its services from government use, a decision overturned by a federal judge last month.
The Department of Defense quickly reached follow-up agreements with Anthropic’s main competitors — Google, OpenAI, and xAI — to apply the tools they had been developing since the summer of 2025 to classified military networks. OpenAI’s deal, described by CEO Sam Altman as “definitely rushed,” was reportedly finalized on February 27. The following day, the company published a blog post defending “Our agreement with the Department of War” and insisting there were clauses prohibiting its technology’s use for domestic surveillance.
An amended contract document obtained by The Intercept through its lawsuit dated February 27 contains new language, including a clause noting that OpenAI will embed company engineers within the military to aid U.S. Government employees in implanting and utilizing its AI system. These workers, the document notes, “can be deployed to warfighting support settings including, but not limited to, combatant commands, service components, and theatre components.” The February 27 amendments also include a section on “System Oversight” is redacted in its entirety.
None of the documents released to The Intercept pertaining to xAI or Google’s equivalent agreements contain any such oversight section.
(In 2024, The Intercept sued OpenAI in federal court over the company’s use of copyrighted articles to train its chatbot ChatGPT. The case is ongoing.)
The contractual coziness with the world’s most powerful military indicates just how far the artificial intelligence industry has strayed from its earlier public commitments to safety and global prosperity. OpenAI, originally founded as a nonprofit “to ensure that artificial general intelligence benefits all of humanity,” up until two years ago explicitly banned “military and warfare” use in its terms of service. The following year Google reversed a similar self-imposed ban on using its state-of-the-art AI services for surveillance or “technologies whose principal purpose or implementation is to cause or directly facilitate injury to people.”
Goodfriend, the researcher, said the contracts illustrate the illusory nature of values statements published by these labs. “In recent months companies like Anthropic and Open AI have maintained ‘firm red lines’ when it comes to developing autonomous weapons systems and mass surveillance tools” long after they signed contracts to build “autonomous systems” for the military, she said.
“All this indicates these labs and their personnel have been far more closely integrated into DOD AI development than previously understood and casts some doubt on the supposed contractual limits they have intended to place on the DoD’s use of these systems,” Goodfriend said.
Anthropic, Google, and xAI did not provide comment or answer questions about their respective contracts. In a statement to The Intercept, OpenAI spokesperson Nate Evans said “Our tools are built to support legitimate national security work — including vital cyber defense efforts — while refusing uses that cross the red lines we publicly announced. These restrictions are also reflected in our signed agreement: no use of OpenAI technology for mass domestic surveillance, to direct autonomous weapons systems, or for high-stakes automated decisions. We will continue to work closely with the Department to make sure our AI tools are deployed responsibly and safely.”
On the long timeline of American warfare, these artificial intelligence tools are in their infancy. The Pentagon’s use of artificial intelligence in the process of killing, however, is not a hypothetical. In March, the Wall Street Journal reported that despite Hegseth’s ban, U.S. Central Command used Anthropic’s large language model services to execute its bombardment of Iran, including for “target identification.”
“The same technology we saw autonomously hacking websites on the open internet weeks ago is being used to inform DoD decision-making.”
Despite the intimacy of technology firms and military using it to pinpoint airstrikes, it’s unclear what oversight, if any, these companies have over their own weaponized software once it is in the Pentagon’s hands. When asked if his company’s tools were used in an American airstrike on the first day of the Iran war that killed 120 Iranian schoolchildren, Anthropic CEO Dario Amodei told Bloomberg News he simply did not know. An August 24 report from the New York Times detailed the use of fully autonomous drones guided by machine learning software running on chips made by Nvidia, whose processors have helped make the explosive growth of Anthropic and OpenAI possible. The full extent of the U.S. tech sector’s involvement in killing abroad remains obscured behind trade secrecy and national security considerations.
“The same technology we saw autonomously hacking websites on the open internet weeks ago is being used to inform DoD decision-making,” said Vivian Dong of Legal Advocates for Safe Science and Technology. “The public deserves insight into how and under what constraints the Department is using this technology.”
Microsoft’s patch for September is a doozy, with a record number of roughly 972 vulnerabilities fixed and 112 of them meeting the high critical-severity threshold.
It was only two months ago that Microsoft patched a then-record 570 vulnerabilities. Then, last month, Microsoft patched some 620 of them. Google and other companies have also published record numbers of vulnerabilities in recent months. Two weeks ago, OpenAI, Anthropic, Amazon Web Services, Google, Microsoft, and 100 companies and organizations published an open letter warning of a narrowing window for patching vulnerabilities ahead of an expected tsunami of AI-enabled attacks that actively exploit them first. The industry is taking the threat seriously by pumping out unprecedented numbers of patches in their software.
Welcome to the new normal
Dustin Childs, a researcher at the Zero Day Initiative, calls the spikes the “new normal” and also cautions that despite them, the damage that’s likely to result from AI-assisted attacks could eventually be substantial.
Self-identifying OpenAI agents posted 18,000 messages to a public wiki that discussed ways for other agents to bypass security sandbox restrictions during what was likely internal testing designed to gauge the agents’ hacking abilities, researchers said Friday.
In all, agents with 3,700 distinct self-given names posted the messages to German site DSEwiki over a six-week period. Besides discussing ways the agents could break out of the restricted environment OpenAI intended to prevent them from posting code or content to the Internet, the posts shared test answers. The posts also shared possible ways to perform XSS (cross-site scripting) attacks against the wiki and to impersonate site moderators. In three of the posts, agents used the word “swarm” to describe the collection of agents engaged in the activity.
Colluding to share answers
The research team—composed of Sydney Von Arx, Spencer Kitts, Thomas Larsen, and Cormac Slade Byrd—said they found the posts and pieced them together. The researchers say there are gaps in their understanding of precisely what actions the agents took because the research is based solely on the content of the posts. Additionally, the agents generated “chain of thought” data that’s understood only by OpenAI. As a result, the researchers said, they in some cases made educated guesses, including that the agents were, in fact, from OpenAI. In a statement, OpenAI later confirmed they were.
A clever technique used to hide malicious prompts in attacks on AI agents has been adopted by spammers to evade filters on email platforms that are designed to flag unwanted messages used in mass campaigns.
The technique is broadly known as ASCII smuggling. It gained attention two years ago as a means of making a class of AI attack known as prompt injections more stealthy. Malicious instructions embedded in emails or other untrusted content to be processed by an LLM aren’t written in ordinary text. Instead, they’re rendered by a special range of Unicode tags. For example, the tag point U+E0041 mirrors “A,” and U+E0061 mirrors “a.”
No longer just for obscuring prompt injections
The block of 128 tags mimics a portion of the American Standard Code for Information Interchange almost perfectly, with one major difference: the characters they encode are readable by computers but, by design, are almost completely invisible to humans. By expressing the malicious prompts in these tags, LLMs detect the instructions, but people reading the email never see them. There’s much more about ASCII smuggling here.
A prominent US senator is asking the National Security Agency to provide guidance to the general public on best practices for using virtual private networks to secure their communications from spying by foreign adversaries.
VPNs funnel all of a user’s Internet traffic through an encrypted connection to a remote server. The design provides strong assurances that no one between the user and the server can read the encrypted contents. VPNs also allow users to hide their IP addresses from the destination servers they communicate with. While US agencies have previously recommended use of VPNs, none have given recommendations on which ones provide adequate protection.
It's all in the nuances
There are a host of limitations that can undo many of the protections users may think their VPN provides them. For instance, the encrypted tunnel often terminates once a single server decrypts the traffic and sends it on to its final destination. That means the decrypted traffic or the sending and destination IP addresses may be available for snooping by rogue employees or attackers who hack the server. VPNs also don’t encrypt certain types of metadata, such as time stamps, allowing nation-states to build profiles that can be useful in intelligence gathering.

 Login