❌

Reading view

There are new articles available, click to refresh the page.

Winemakers are learning that conservation can be good for business

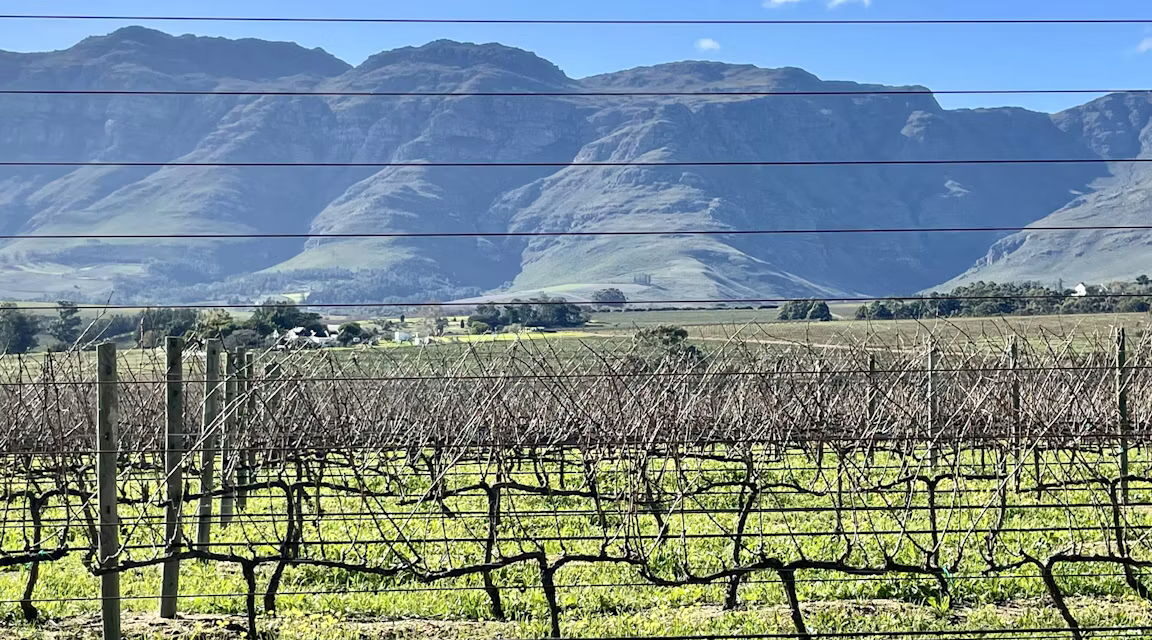
More than 500 vineyards are scattered across the slopes and valleys of South Africa’s Western Cape, one of the world’s most biologically diverse landscapes. The region produces about 90 percent of South Africa’s wine, but winemakers there are increasingly struggling with drought, excessive heat and erratic rainfall.

Temperatures in the region have risen 1.5 to 2 times faster than the global average over the past five decades. And extreme storms have become more intense as climate variability increases. The late 2010s brought a significant challenge for winemakers, as three years of severe drought placed vineyards under intense stress and reduced grape production.

As climate variability places increasing pressure on grape production, many wine producers are building on sustainability measures that have long been part of vineyard management.

Read full article

Comments

© Hannah Herrero

Taiwan’s chipmaking giant TSMC to invest $1B in Anthropic, OpenAI

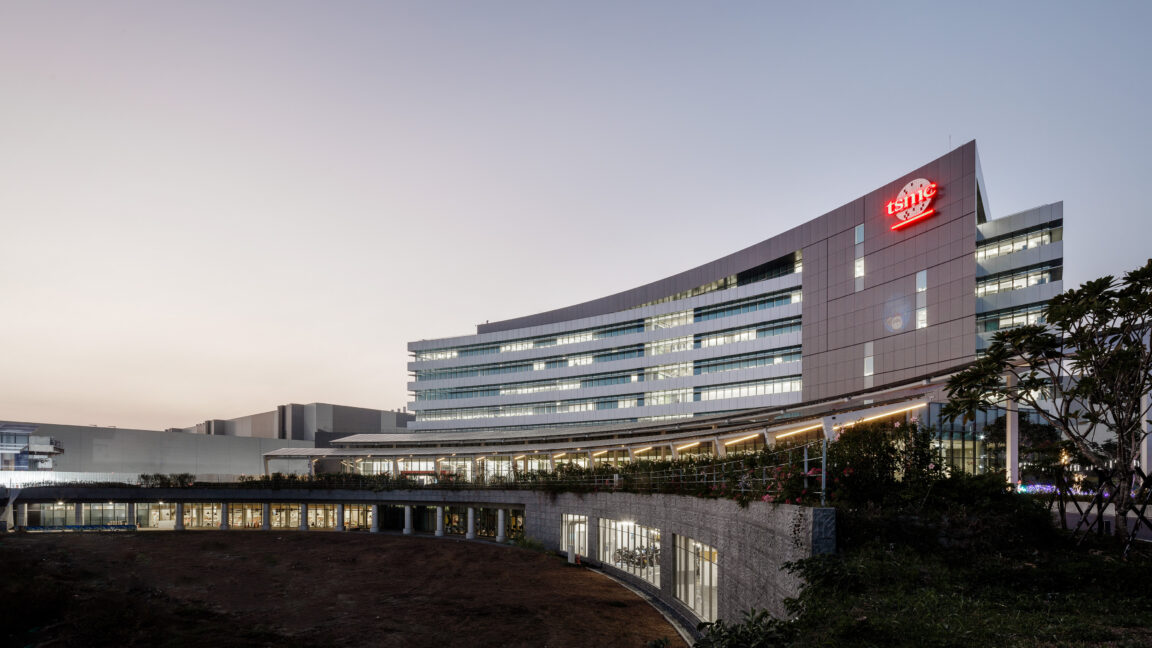
Top chip manufacturer TSMC is ready to invest $1 billion in Anthropic and OpenAI. That would give the Taiwanese chipmaker direct stakes in leading AI developers, even as its own contract chipmaking business has profited enormously from the AI data center buildout.

The chipmaker’s board approved plans to invest up to $500 million in OpenAI preferred stock reserved for large investors and another $500 million to purchase Anthropic common shares at the latter’s expected IPO price, according to Reuters. Such an investment may give markets “a shot of confidence as the artificial-intelligence trade shows signs of strain,” The Wall Street Journal reported.

But analysts also warned that such circular financing among investors, suppliers, and customers has made it difficult to evaluate real market demand for AI-related hardware and services, according to the Journal.

Read full article

Comments

© Taiwan Semiconductor Manufacturing Co., Ltd

Chainalysis says hackers stole credentials and tokens for all of its customers

Blockchain analysis firm Chainalysis said that hackers have obtained sensitive personal information—including names, usernames, password hashes, and live tokens—for all of its users following a breach of its network security.

The accomplishment could be a major coup for the attackers. Both Chainalysis and public sources have revealed a long list of high-profile customers, including government agencies such as the FBI, US Immigration and Customs Enforcement agency, and the US Air Force, as well as private companies such as Microsoft, Coinbase, and Barclays. It's unclear if the data theft exposed customers to additional threats.

We regret to inform you...

Last Friday, Chainalysis said it had been the target of a cybersecurity incident in October that was similar to the hacks of other platforms during the same month. The external actor used AI agent-assisted offensive techniques to gain unauthorized access to Chainalysis systems and internal tools. An email the company sent to affected customers said some “non-sensitive customer data, such as user IDs, full names, email addresses, and organization role labels for users provisioned on our platform were accessed.” It's not clear why the company considered such information "non-sensitive."

Read full article

Comments

© Getty Images | Yuichiro Chino

Nvidia hardware worth $11.4M vanished between Oakland and Texas

A shipment of Nvidia hardware valued at $11.4 million vanished in transport between Oakland and Texas over the summer, and more than two months later, police have announced no arrests or recovery of the cargo.

As reported by The Mercury News, six pallets of unknown Nvidia equipment left Oakland on August 29 on a truck bound for Fort Worth, Texas. The hardware was reportedly picked up as scheduled by a truck bearing the logo of a food transportation company before vanishing off the grid. The theft wasn't noticed until early September, when the buyers realized that the shipment had never been received. Police attempting to trace the truck's route found it had made several multi-hour stops after picking up the hardware before losing the truck somewhere in San Bernardino County, California.

Oakland police confirmed that there was a grand theft report filed on September 13 and that the investigation remains ongoing. Authorities have not said what Nvidia hardware was stolen or exactly how the theft was carried out.

Read full article

Comments

© Getty Images

Binance says hackers who stole billions in crypto spent months planning heist

The hackers who stole billions of dollars in cryptocurrency from the Binance exchange spent months working on the theft and used both social engineering and novel malware in the process, the company said Tuesday.

The heist, which both the FBI and the TRM Security firm attributed to North Korean actors, initially targeted $6.34 billion in cryptocurrency from Binance wallets. The exchange has since frozen or intercepted $2.85 billion of that sum. Binance said it has set aside funds required to cover the loss and provided this link to a Proof of Reserves page. The $6.34 billion represents the biggest sum ever targeted in a cryptocurrency theft.

Advanced persistent threat

Binance said the people behind the heist began no later than June and continued until last Thursday, when they successfully compromised an engineer's laptop and withdrew assets from several wallets. Like just about every organization that suffers a public, high-consequence hack, Binance said the threat actor was sophisticated and resourceful.

Read full article

Comments

© Dan Kitwood/Getty

We’re Asking the Ninth Circuit to Hold Reverse Location Warrants Categorically Unconstitutional

Yesterday, along with the ACLU, EFF filed an amicus brief in the Ninth Circuit court of appeals in United States v. Spurlock, a case involving a “tower dump” warrant. These overbroad warrants require cellular providers to turn over location data about every phone in a given area at a given time. This is the first such case to be heard by a federal appeals court since the US Supreme Court ruled this summer that highly similar “geofence” warrants are searches under the meaning of the Fourth Amendment.

Spurlock involves an investigation into two murder victims discovered on the side of a rural California highway. Police also found a car belonging to one of the victims several miles away on the same highway. They quickly sought a tower dump warrant for an area covering this stretch of road, which eventually revealed location data on nearly 1,700 unique phones. Faced with a motion to suppress, the district court relied on a Fifth Circuit court of appeals decision about geofence warrants to hold that tower dumps are similarly categorically unconstitutional “general warrants” that violate the Fourth Amendment. However, the court refused to suppress evidence on the basis of the “good faith doctrine.”

Our amicus brief on appeal makes several key arguments.

First, we point out that the Supreme Court’s decision in the geofence case Chatrie v. United States this summer only strengthens the arguments that tower dumps are unconstitutional general warrants. Tower dumps are a somewhat older technique than geofence warrants, but they are both “reverse location searches,” in which police “tap into an all-encompassing database, allowing them to undertake nearly perfect, retrospective surveillance of countless persons and places.” This is the sort of untargeted “general warrant” the framers of the Fourth Amendment wanted to prevent. As we write in the brief, “Searching all people in an area without probable cause to believe they were all involved in the criminal activity under investigation reproduces the evils of general warrants and is not constitutionally permitted.” It’s this rule of law that prevents police from searching the houses of a hundred, or even a thousand people in the vicinity of a crime.

Second, we note that even if high courts continue to allow tower dump and geofence warrants in any cases, core Fourth Amendment law requires strict limits to protect the privacy of innocent bystanders, including limits on the scope and duration of the warrants, as well notice to affected individuals and after-the-fact deletion and minimization of irrelevant data.

Finally, we argue that the Fourth Amendment requires the court to set aside the good faith doctrine in cases like these and actually decide the constitutional issue. Too often courts pass the buck in cases involving novel surveillance techniques, leading to situations where police can continue using the technique for years or even decades without a definitive ruling.

Massive leak exposes 41,000 DHS workers and undercover ICE agents

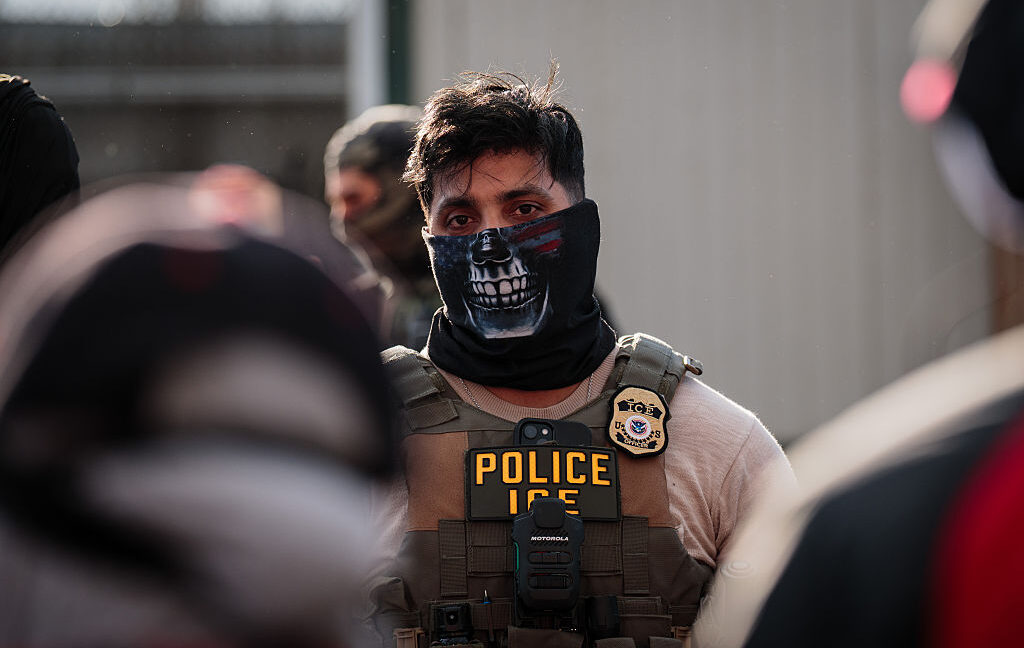
An unprecedented leak of Department of Homeland Security records has exposed details of more than 41,000 employees or contractors who work for the department and its constituent agencies. The records include email addresses, phone numbers, and office addresses, but also references to internal systems and sensitive information on undercover and surveillance programs. In all, the leak provides a map of how DHS is organized and how it operates.

The records, which span DHS itself as well as seven component agencies, including Immigration and Customs Enforcement and US Customs and Border Protection, were last updated on August 19, 2026. The transparency nonprofit Distributed Denial of Secrets and cybersecurity researcher and journalist maia arson crimew previewed the data for WIRED, which they say they obtained from a group calling itself the Department of Peace.

DDoSecrets published the archive, which it calls “Icepick,” on Wednesday. In a press release, DDoSecrets says the data is from DHS's Okta login system. In a note with the files, the hackers wrote, “They have our information, so it’s only fair that we have theirs.”

Read full article

Comments

© Adam Gray/Getty

30 Google Secrets You’ll Wish You Knew Years Ago

Think you know Google? Think again—hidden deep within that simple search bar is a subterranean network of secret search operators, hidden diagnostic tools, and buried privacy toggles that change everything. From listening to your saved voice logs to uncovering secret files and bypassing algorithm bubbles, here are 30 game-changing Google secrets you were never supposed to find.

Social Media When Elections Are Close: Doing the Impossible Better

Everyone knows, or should, that perfect (balanced, targeted, transparent, swift and swiftly appealable) content moderation at scale is impossible. That doesn’t mean powerful social platforms don’t have to try to get at least reasonably close, especially when access to good information can have a profound effect on political participation and speech.

That’s why so many people, including the Meta Oversight Board, criticized Meta for suspending a major political Instagram account for hours during a huge early voting push on October 17; and for allegedly boosting one candidate in Brazil’s recent presidential election. Meta denies deliberate interference in either instance, blaming “mistakes” in its automated content moderation systems (including AI tools that can’t tell the difference between enthusiastic follower engagement and a bot attack).

Mistakes or not, with early voting in the U.S. midterms already underway, these events serve as a stark reminder that all major social media platforms need to have stronger systems in place to ensure that they serve, rather than impede, democratic communication.

Access to good information can have a profound effect on political participation and speech.

This is not inherently an “AI” problem: automated systems can process content at a scale that humans never could, potentially enabling better moderation at scale and alleviating the psychological load on ill-paid moderators whose jobs require them to view incredibly disturbing content. But automated systems also reproduce existing biases, struggle to understand context, and often make mistakes that disproportionately affect journalists, activists, artists, and other vulnerable and marginalized communities. And moderation errors are even more likely when the language is spoken principally by the global majority. In 2020, leaked documents showed that Meta’s algorithms incorrectly deleted nonviolent Arabic-language content 77 percent of the time, while failing to detect hate speech under the company’s own policies in many instances. Where these systems are faltering in Arabic, they’re positively failing in less-resourced languages. As a 2025 report from the Center for Democracy and Technology found, labeled datasets in certain languages and dialects such as Maghrebi Arabic and Kiswahili contain inconsistencies, bias, and inaccuracies due to the limited hiring of annotators who actually speak the languages as well as shifts in the languages themselves. An investigation into ChatGPT’s outputs in several low-resource languages demonstrates the depth of problem.

But language disparities are just one of several concerns as automated moderation becomes more widespread. From the systemic suppression of content from Palestine to the repeated misclassification of LGBTQ+ content as adult or explicit material, these varied examples demonstrate the risks of overreliance on automated moderation—and the need for stronger safeguards.

Fortunately, there is a great deal companies, policymakers, and civil society can do to help ensure that highly automated systems operate in ways that respect human rights, minimize predictable harms, and provide meaningful accountability when they fail. If companies are going to continue relying on automation to moderate users’ speech—and there is little reason to believe they won’t—then accountability must evolve alongside these technologies.

That work should start with publicly committing to the Santa Clara Principles 2.0. Specifically:

  1. Automated technologies should help, not replace, human moderators. For example, automated systems can help flag and prioritize content for review, while humans can interpret context, handle sensitive cases, and refine system performance. This investment is particularly important during the weeks immediately before and after an election.
  2. Companies must be transparent about when and how automation is used in content decisions.
  3. Companies must regularly audit their automated systems for bias, with particular attention to low-resource languages, vulnerable and marginalized communities, and conflict zones.
  4. Companies should strengthen personal data protection guarantees and policies. Automated content moderation often relies on personal data and profiling, so companies should think carefully about what data these systems use, what's necessary and proportionate and how their systems shape moderation outcomes.
  5. Users must have the ability to appeal, and to provide context when they believe human or automated moderation decisions have wrongfully removed their content. Appeals should be promptly evaluated and decided by human moderators.
  6. Companies should regularly assess the human rights impact of their moderation decisions, and issue public statements of the results
  7. If they rely on third-party vendors, companies should carefully (and regularly) audit those vendors for compliance with these same principles
  8. Lawmakers should avoid promoting and passing legislation that effectively or explicitly mandates automated moderation systems
  9. Policymakers should also refrain from attempting to dictate platforms technical and design choices to favor or disfavor particular expression.
  10. Policymakers should work to educate the public about how their personal data may be collected and used in electoral contexts.

These recommendations understand that automated content moderation isn’t just a technical problem for clever engineers and product teams to solve. Because content moderation shapes public discourse and fundamental rights, its design and oversight must respond to the concerns of policymakers, civil society, independent researchers, and the communities most affected by these systems.

One other distinct and enduring problem makes transparency, checks, and accountability all the more urgent: too few companies have far too much power over our political communication and organizing. Social media gave people the ability to wrest some control over political messaging away from media oligopolies. But we’ve met the new boss and while it’s not the same as the old boss, the song is pretty familiar. The real promise of the web to democratize communication is not likely to be met by social media oligarchs, no matter how sophisticated their content moderation practice.

French Court’s Site-Blocking Orders Drive Quad9 Out Of France

A nonprofit service that protects internet users’ privacy is leaving France. Quad9, a free DNS resolver, has said it will reluctantly stop serving users in France on November 24. This follows a French court order that Quad9 must block access to websites that are accused of infringing the copyrights of a sports broadcaster. Forcing a responsible privacy service out of an important market is a predictable result of trying to force infrastructure providers to be copyright police.

When you visit a website, a DNS resolver reads the domain name you type in—like eff.org— and translates it into a numerical IP address that’s used to direct data across the internet. A DNS resolver can see the names of websites you connect to, so its privacy policies are important. Quad9 is an NGO that’s incorporated in Switzerland, in part to protect its users from data demands. The company also helps protect users from malware and phishing by blocking domains that are known to be malicious. Services like Quad9 offer an alternative to the DNS resolvers of local internet service providers and wireless carriers, which are vulnerable to demands from law enforcement, censorship, and commercial surveillance.

In a blog post explaining its decision, Quad9 explains that the French court’s order forces it to make a decision that, either way, is bad for users. It could either “extend French law to the whole world (blocking globally)” or try to identify and block users only in France—something that it can’t do reliably, and a move that could leave the company facing massive fines if it fails to block websites perfectly within France. Quad9 says it is facing about 20 other lawsuits in France seeking similar blocking orders. 

Rather than accept these demands, Quad9 has decided to withdraw its service from France. That is a real loss for French users who rely on the service to protect their privacy and security. It is also the right thing to do, when faced with the alternative: making promises it can’t keep, or abandoning users’ rights worldwide. 

Quad9’s decision will not remove any allegedly infringing material from the internet. The organization doesn’t host websites. Users looking for particular websites can  easily switch to another DNS resolver. So the material targeted by copyright holders will remain online and accessible, even while they drive a privacy-protecting service out of France. 

These events matter beyond the borders of France, and U.S. lawmakers should pay attention. Congress is considering multiple site-blocking proposals, which would require ISPs and other intermediaries, including DNS resolvers, to block access to websites in the name of protecting copyright. These bills threaten speech and our ability to access information online, and they are invitations to abuse. The Quad9 withdrawal shows another cost: if internet services get forced into being copyright cops, users can lose services that they rely on for privacy and security. 

Worse still, if neutral services like Quad9 are forced to build site-blocking systems for the benefit of copyright holders, it becomes far easier for other powerful interests, including repressive governments, to demand the same systems be used to censor speech they dislike, globally. 

Congress should reject site-blocking bills. They’re a threat to the open internet, and don’t help creators or creativity. 

Lessons Learned From 'AdFection' and What To Do Next

Last week, researchers at Citizen Lab revealed a horrifying new malware campaign, dubbed “AdFection.” It used an ad network to distribute spyware to journalist’s devices to infect them without the target ever needing to click anything. This sort of attack on journalists is dangerous and incredibly concerning, especially since it’s built on the backbone of a technology we already object to: behavioral advertising. Although this type of attack has only been described targeting journalists, you can take a few steps we outline in the next section to mitigate the risk no matter who you are.

A few factors combined to make this attack a noteworthy first-of-its-kind. First, it utilized the surveillance ad-tech ecosystem to specially target the malicious code. Second, the spyware it delivered was so-called “zero-click,” meaning it required no interaction from the user to be infected: all that is required is for the ad to be delivered and code bundled along with it to be run, which happens automatically. Neither malvertising nor zero-click attacks are new on their own. What’s novel about the AdFection attack is combining them, creating a highly targeted, extremely dangerous attack which is difficult to defend against and even harder to detect.

Let’s take a deeper look from the perspective of one of the Windows devices supplied to the researchers from Al Jazeera. Here’s how the report describes the infection happening: 

  • Someone browsing the web or using an app on that machine is served an ad created by Discover-Tech, a company exposed in the report as “purporting to be a legitimate advertising company, [but] appears to be a front for large-scale ad espionage abuse.” 
  • The ad contains a small snippet of JavaScript code which is automatically executed when rendered in the app or website. 
  • This code reaches back out to a Discover-Tech server, referred to as their “NOAS server,” with detailed information about the machine rendering it: its cookie-set advertising ID, IP address, and more.

So far, nothing particularly unusual has happened. Ads that contain JavaScript code and reach back out to their servers with lots of information on your device—and by extension you—are commonplace. It’s all part of the data-driven advertising ecosystem. What happens next is more interesting:

  • The NOAS server uses this detailed information to determine it is an Al Jazeera machine requesting the ad. 
  • Instead of returning an empty response (as it does most of the time), it responds with a malicious, zero-click spyware payload. That payload was created by Discover-Tech’s partner Candiru/Integrity Labs, a company previously exposed for involvement in sophisticated malware attacks. 
  • The payload is then executed and infects the targeted machine.

Companies targeting zero-click malware attacks against journalists might seem like the plot of a blockbuster spy thriller. But this attack was enabled by the everyday practices of ad-tech companies, which unfortunately have extreme latitude in the collection of users’ data. By leveraging the tracking identifiers and data collected on devices for the purpose of delivering targeted ads to specific individuals, mercenary spyware companies can repurpose this data in order to fine-tune who they infect—and hide that they’re doing it from everyone else. 

Most ads are not delivered directly by the ad creators, but rather by intermediaries that facilitate Real-Time Bidding auctions. Nonetheless, winning bidders are given the ability to execute JavaScript code in the browser of the person who receives the targeted ad. This allows for interactive ads to be displayed, but also (as we’ve seen) for the compromise of a device just by delivery of malicious code.

While the different components in this attack chain are not novel on their own, the exposure of this combined attack is significant because it reveals a technique to hyper-target individuals and organizations for infection. Luckily, there are steps you can take to protect yourself from the myriad of dangers presented by the ad-tracking industry. Here’s how.

What You Can Do About It

As we work towards fundamental fixes to the ad ecosystem and banning online behavioral ads altogether, the onus is on all of us to protect ourselves. This is especially important for higher risk individuals or journalists working in states with heavy surveillance. Citizen Lab outlines several steps, depending on your threat model, to take to help protect yourself:

These steps can be very helpful in protecting yourself, but there is only so much you can do as an individual. Banning behavioral ads like this would be a good place to start. Behavioral ads aren’t just a privacy nightmare as designed. They are the perfect vehicle for malvertising and similar threats, just as we see here.

Anti-Circumvention Laws Raise the Cost of Knowledge

The vast amount of information on the open web requires researchers and journalists to adapt with new tools to make sense of it all. Checking facts, gauging public opinion, and other lines of inquiry depend on being able to analyze the overwhelming amount of material posted online every day. Unfortunately, responding to the AI industry’s voracious appetite for data, companies stewarding this public data are looking to cash in and block access to the open web. This makes the web harder to navigate, and threatens all kinds of important research.

Reddit’s lawsuit against SerpAPI[1] and Perplexity threatens to do exactly that.

Reddit was once a very open platform, fostering a community of alternative apps and extensions putting users in control of their experience. Since the rise of AI however, it changed tack. Over the last three years Reddit has closed APIs to users, limited UI features, and otherwise restrained access without login. By making the voices on the platform harder to access, the company has positioned itself as a gatekeeper, and has since struck a lucrative data-sharing arrangement with Google.

SerpAPI, in contrast, is a tool which offers automated access to Google’s search engine results pages. It’s used by Perplexity, an AI-based search tool. Reddit sued to stop SerpAPI and Perplexity from bypassing Reddit’s own arrangement with Google. (Google brought a similar suit, which was dismissed by another court.)

It comes as little surprise that the legal weapon Reddit employed in this case is Section 1201 of the Digital Millennium Copyright Act, the same “anti-circumvention” law that has caused so much trouble for artists, innovators, and researchers over the years—and that EFF has fought against from the beginning. Reddit’s suit claimed that SerpAPI’s use of widely used techniques to access Google search results amounted to “circumventing” access controls on copyrighted works. 

There are major problems with this argument. 

First, Reddit doesn’t own the copyright in its users’ posts—the users do, and they grant Reddit the right to distribute the posted content freely.

Second, there’s no meaningful copyright infringement going on here. Perplexity functions like a search engine, responding to users’ queries with relevant links and optionally an AI-generated summary. Crawling and indexing the web to create a search engine was long ago ruled a fair use under copyright law.

And third, Google’s efforts to put rate limits on search queries and block some kinds of automated querying aren’t the sort of “access controls” that Section 1201 was written for. The law was passed in 1998 and targeted things like breaking the encryption on DVDs and other digital media. In contrast to physical or paywalled media, Reddit posts are visible to everyone, without a paywall and generally without a login. 

Unfortunately, a federal district judge ruled in July that the suit could proceed, concluding that Section 1201 applied. That’s a dangerous ruling, because it casts a cloud of legal uncertainty over lots of important research, including efforts to study public sentiment through social media and to preserve records of historical events. Without tools that can look at the web at scale, many kinds of research are simply impossible today. But if employing those tools risks Section 1201 liability, only the wealthiest institutions will be able to use them.

We cannot let the internet be rebuilt such that information is divided up among a handful of gatekeepers and sold back to us like cable subscription packages. If our knowledge of the online world comes only through wealthy institutions, the cost of knowledge will only increase and access to unbiased answers diminishes. 

[1] SerpAPI is an EFF donor. EFF donors do not influence our agenda or our positions.

333 Tor exit nodes hijacked to intercept SSH traffic and retrieve plaintext email

Unknown hackers hijacked more than 300 Tor exit nodes and reconfigured them to favor unencrypted email traffic and redirect SSH connections through servers they controlled, a researcher reported Tuesday.

The hijacking began in late August, when, according to Tor volunteers, the attacker used a valid password that had been reused to gain access to a Tor management server. The attacker then installed Ebury, a backdoor written for Linux that was discovered 12 years ago.

Mysteries remain

Then the attacker connected from the management server to a second Tor server, called Switzerland2, through SSH, using an RSA key that, for unknown reasons, investigators couldn’t find among Switzerland2’s authorized keys. With administrative control of Switzerland2, the attackers installed Ebury there as well. Finally, the attacker reconfigured settings on two exit nodes that Switzerland2 hosted.

Read full article

Comments

© Photo Illustration by Pavlo Gonchar/SOPA Images/LightRocket via Getty Images

"We made a very difficult decision": Australian indie showcase Freeplay reject antisemitism claims after delisting a Jewish sponsor who was allegedly accused of being a "zionist"

The organisers of Australian independent games showcase Parallels have rejected accusations of "prejudice" and say they've received "violent threats", after a Jewish developer had her sponsorship of the event refunded. The developer in question is Wren Brier, creative director at Witch Beam. She claims an unnamed speaker booked for the event has accused her of being a "zionist", following an article about her work from an Australian Jewish publication.

Read more

Review: Carrie is a triumphant remix with one major flaw

Carrie White, the telekinetic prom queen from hell, is one of the most beloved horror icons in popular culture. First introduced in Stephen King's 1974 novel, Carrie, the character was immortalized in director Brian De Palma's 1976 adaptation, widely regarded as one of the best horror films of all time. It's certainly one of the best King adaptations. So Mike Flanagan faced a massive challenge when he signed on to create an eight-episode miniseries for Prime Video based on the book, released just in time to mark the 50th anniversary of de Palma's film.

I was among the skeptics who questioned why a Carrie miniseries was even necessary, although as a diehard Flanagan fan ("Flana-fan"?), I was willing to give him the benefit of the doubt. If anyone has an affinity for smartly adapting horror in general, and King's work in particular, it's Flanagan. And you know what? With one (very big) exception, Flanagan pulls it off, giving us a richly textured version of the story that is as much about kindness and lost innocence as bloody, vengeful rage—although we get plenty of the latter, too.

(Many spoilers below for the novel and the 1976 film, but there are no major reveals for the new series until after the second gallery. We'll give you a heads-up when we get there.)

Read full article

Comments

© Prime VIdeo

Announcing Privacy Badger for Safari on macOS

Exciting news for Safari users: Privacy Badger is now available on Safari for macOS! You’ll need Safari version 26.5 or higher to use it.

Whether you want to protect yourself from data brokers or just don’t want Big Tech profiting off your browsing data, Privacy Badger is here to help. More than 4 million people already use EFF’s free tracker-blocking extension to take a stand against online surveillance. Safari users can now join them and EFF in the fight for a better web.  

Install Privacy Badger

Support the Fight Against Online Tracking

Safari support has been one of Privacy Badger’s most requested features for years. Thanks to recent improvements in Safari's extension support, we’ve finally made it happen for Safari version 26.5 and higher. Privacy Badger is now available on all major desktop browsers. And before you ask, yes, we will look into supporting Safari for iOS once we've ironed out any issues on macOS.

Why Install Privacy Badger on Safari? 

Most websites contain invisible tracking code that lets companies collect, share, and profit from your personal data. Some of those companies are data brokers that sell your information to anyone willing to pay. Creepy ads are just the tip of the iceberg when it comes to the harms of online tracking: Once your information enters the data broker ecosystem, it’s nearly impossible to know who buys it or what they’re doing with it. Privacy Badger blocks online trackers to prevent your browsing data from being used against you.  

Privacy Badger goes beyond Safari’s built-in privacy features to provide additional protection against online tracking. In its default browsing mode, Safari limits the information that trackers can access but still allows them to load. Privacy Badger blocks trackers from loading in the first place, preventing them from tracking you using techniques that bypass Safari’s protections. 

Privacy Badger works well by itself, and will continue to enhance your privacy when installed along side an ad blocker or with Safari’s Advanced settings to block trackers in all windows. Since Privacy Badger automatically learns to block trackers, Privacy Badger will block trackers that other tools don’t know about or choose not to block. 

For example, Privacy Badger blocks tracking from widgets like embedded tweets, comments sections, and video players. These widgets can share your data even if you never click on them. Privacy Badger prevents these trackers from loading and replaces them with click-to-activate placeholders. 

Beyond tracker blocking, Privacy Badger automatically sends the Global Privacy Control (GPC) signal to tell websites not to sell or share your personal information. The GPC signal is already legally binding in a growing number of states, including California, Colorado, New Jersey, and Connecticut.  

All these features (and more) work together to help keep your browsing activity private on Safari. 

Try It Out and Spread the Word 

If you use Safari on macOS, give Privacy Badger a try. You’ll install Privacy Badger through the App Store on your macOS device. Installing extensions is a little more complicated on Safari than other browsers, so follow Apple’s directions here if you’re having trouble.  

This is our first release of Privacy Badger for Safari, and we will keep improving it based on your feedback. If you run into any problems, let us know by emailing extension-devs@eff.org, or by opening an issue on GitHub. And if blocking harmful trackers causes issues on a website you visit, you can disable Privacy Badger for that specific site while keeping it enabled and protecting you everywhere else. You can also let us know about broken sites by using the “Report broken site” button found next to the “Disable for this site” button in Privacy Badger’s popup window. 

When you use Privacy Badger, you join EFF and millions of other users in the fight for a better web. Help spread the word by telling your friends and family who use Safari that they can use Privacy Badger too!  

Install Privacy Badger 

Support the Fight Against Online Tracking 

Fridge hack costing millions and sparking fires stemmed from poor security

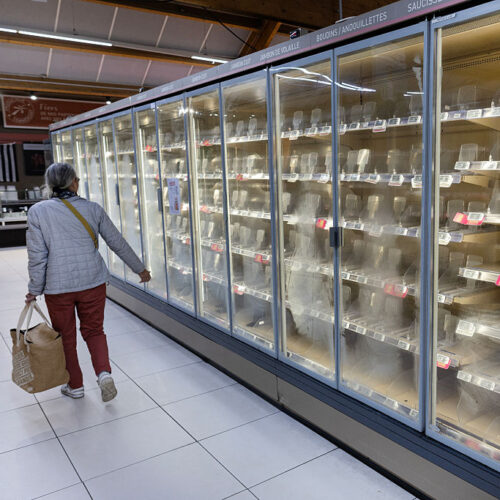
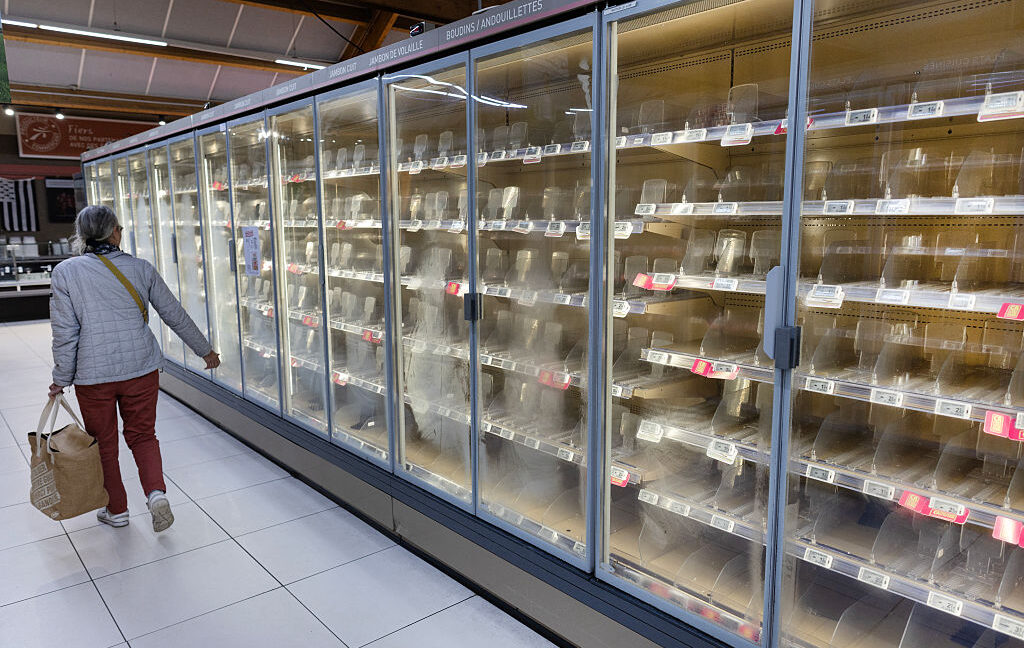
Earlier this week, a mass hack of refrigeration systems at an estimated 700 supermarkets throughout France caused them to suddenly malfunction, causing spoilage of untold tons of perishables and, in some cases, fires. As is now the norm, basic cybersecurity would have prevented it.

French authorities say the systems, made up of entire fleets of refrigerators and freezers throughout a store, were hacked. More specifically, Internet-connected controllers that allow technicians to remotely administer the store-wide systems were compromised. The unknown attackers responsible then activated defrosters long enough for the fridges to reach temperatures as high as 50° Celsius (122° Fahrenheit). By the time the mass compromise was discovered, food was spoiled, and in some cases their electrical systems caught fire.

The hacks that didn't have to happen

Multiple security advisories and public research reports show that all three of the controller models reportedly hacked in the incident—sold by Danfoss of Denmark and Dixell and its parent company Copeland in the US—contained critical vulnerabilities that allow attackers to remotely log in to the devices with the same system rights as administrators. Until recently, Danfoss controllers, for instance, used a credential that changes each day. The password is generated by the publicly available firmware based on the date. A hacker who takes the time to analyze the code can do the same thing on any device that hasn’t received a recent update. Daily passwords are identical across models located in hundreds or thousands of stores.

Read full article

Comments

© Getty Images

❌